Uncategorized
Ledger Live Windows – What the App Does with Your Keys
Ledger Live Windows installation is a short process, but the order of the steps matters: get the app from ledger.com, connect your Ledger device by USB, and let the app load your accounts before you move any funds. This guide explains what the app does with your keys, how a Windows PC differs from other platforms, the first-week mistakes that cost money, and what to do when you move to a new computer.
What Ledger Live Does with Your Keys on Windows
Ledger Live is only the interface. Your private keys are generated and stored on the Secure Element of your Ledger device and stay offline. The app builds transactions, shows balances, installs coin apps and passes each transaction to the device. Every outgoing transaction must be checked and physically confirmed on the device.
Where signing happens
Signing happens inside the device, never on the computer. A hostile program on the PC could propose a transaction, but it cannot produce a valid signature without your physical confirmation on the device.
Why the device screen outranks the monitor
Malware can alter what appears on a computer screen, including the recipient address. The device screen is the one you can trust. Read the address and amount there before you confirm.
What stays on the computer
Ledger Live keeps local app data, such as preferences and your account view. It is not a backup of your funds. Your backup is the 24-word recovery phrase that you wrote down offline, so treat the PC data as replaceable.
Setting Up Ledger Live on a Windows PC
Follow these steps in order the first time.
Step 1: Install from ledger.com
Type ledger.com into the address bar rather than clicking a search ad, then open the Ledger Live page and choose the Windows version. Check the current system requirements listed there. If a page asks for your recovery phrase while offering a download, it is not Ledger.
Step 2: Connect the device by USB
Use a cable that carries data, plug the device into the PC and enter your PIN. Supported devices are the Nano S Plus, Nano X, Ledger Flex and Ledger Stax. The original Nano S is discontinued, although existing devices still work. Bluetooth is not used on desktop.
Step 3: Set up the device
A new device generates its 24-word recovery phrase on its own screen during setup. Write it on paper or metal and store it offline. Ledger Live will never ask you to enter your 24-word recovery phrase.
Step 4: Install coin apps and add accounts
Open My Ledger, install the coin apps you need, then add accounts in Accounts. Generate a receive address and compare it with the device screen before you share it.
Windows Compared with Other Ledger Live Platforms
Every version of the app reaches the same keys on the same device, so the choice depends on the connection, the source of the download and how you work.
| Platform | Where to get it | Connection to the device |
|---|---|---|
| Windows | ledger.com | USB |
| macOS | ledger.com (not the Mac App Store) | USB |
| Linux | ledger.com | USB |
| iOS | Apple App Store | Bluetooth with a Nano X (and, where Ledger supports it, newer devices) |
| Android | Google Play (an APK only from ledger.com) | Bluetooth with a Nano X; USB where supported, check ledger.com |
A Windows PC suits long sessions with several accounts, a wired connection and a large screen. A phone suits quick checks and approvals away from a desk. Neither replaces the device, because every transaction still ends with a confirmation on it.
Computers that are poor hosts
Shared office computers, kiosks and PCs with remote access software are poor hosts for any wallet app. The environment is more often the weak point than the app. Use a computer that only you control and keep Windows updated.
Mistakes That Cost Money in the First Week
The costly failures come from human steps, not from software, and none of them can be reversed once a transaction is confirmed.
Typing the recovery phrase anywhere
Never type your 24-word recovery phrase into a website, a chat, a text file or any app. Anyone or anything asking for it is a scam. Restoring a wallet happens only on the device itself. Do not photograph it, take a screenshot or keep it in the cloud.
Downloading from ads or unofficial pages
Fake download pages and fake apps are a known phishing method. Look-alike domains copy the look of the real page. Typing ledger.com yourself, or using a bookmark you saved earlier, removes the ad from the path.
Approving a transaction without reading the device
Malware can change an address that you copied. Compare the address and amount on the device screen with what you intended, and reject the transaction if anything differs.
Moving Ledger Live to Another Windows PC
Your crypto is controlled by the keys on your device, so moving the app does not move coins. On the new PC, install Ledger Live from ledger.com, connect the device, enter your PIN and add your accounts again. If you lose the device, a new Ledger device can be set up from your recovery phrase, but that restoration happens on the device itself, never in the app. Ledger Recover is an optional paid service with details on ledger.com. If you forget the optional password lock, reinstall Ledger Live and reconnect the device.
Updates and What Changes Over Time
System requirements, supported coins and menus change with releases. Confirm details on ledger.com instead of old tutorials. Device firmware is never downloaded as a separate file; it is installed through Ledger Live in My Ledger by following the prompts on the screen and on the device, without disconnecting during the update.
Frequently Asked Questions
Can I install Ledger Live on a Windows PC without administrator rights?
The installer may need approval from an administrator on a managed PC. Ask the person who manages the computer to help. Do not use modified or “portable” builds from other sites, because they do not come from Ledger.
What should I do if the installer is blocked or Windows shows a warning?
Do not bypass the warning and do not turn off your security software. Delete the file and download it again only from ledger.com. If it continues, contact Ledger Support through ledger.com.
How can I tell that the Ledger Live Windows installer is genuine?
Type ledger.com yourself and get the app from there. Avoid search ads, mirrors and links sent in chats. If a copy came from anywhere else, delete it.
My Ledger device is not detected after setup. What should I try?
Unlock the device with your PIN, plug it straight into the PC with a data cable, and try another port. Close other programs that may use the device and restart Ledger Live. There is no separate driver or bridge to install.
Can I move my accounts to another Windows PC?
Yes. Install Ledger Live on the new PC, connect your device and add the same accounts again. The balances load from the network.
Should I reset my device if Ledger Live does not see it?
No. Do not reset the device as a test. Check the cable, port and PIN first, and contact Ledger Support through ledger.com if the problem continues.
Ledger Live Download for Mac: A Safe User Guide to Genuine Installers
Ledger Live Download for Mac Safe User Guide opens with the only rule that decides everything else: take the installer from the publisher’s own domain and check its signature before you open it. Every section below supports that single step. You get the verification procedure, the routes that fail it, the limits of what the software can protect, and the details that shift between releases.
Two things run side by side on an Apple computer: an interface that reads public data, and a hardware signer that holds the keys. The first can be replaced by any convincing lookalike; the second cannot be cloned by software at all. That asymmetry is why origin checks carry more weight here than in an ordinary install.
Set aside twenty minutes, a network you trust, and the device itself. The checks further down this page use only tools that already ship with the operating system.
How the desktop client works on Apple hardware
The application is a front end that holds no private keys. It reads balances from public blockchain data, builds a transaction, and sends it to a connected signer; the signer shows the amount and destination on its own screen, and only then does it sign. Your computer sees addresses and signed payloads, nothing more.
Where the interface stops and the signer starts
The split is enforced by the device, not by the software, so a modified client cannot quietly approve a payment on its own. When you press send, the payload travels over USB or Bluetooth to the signer, which decodes it and renders the recipient address and amount on its display. You compare what you typed with what that screen shows. If the two differ, the transaction is rejected at that moment, and no amount of tampering on the computer changes the outcome.
What lands on disk after installation
A single application bundle goes into the Applications directory, while the client writes its database, cache and logs into a folder inside your home library instead of scattering files across the system. Removing the bundle alone leaves that data behind, which is why a clean reinstall also means deleting the support folder. The bundle carries a code signature and a notarization ticket, and the operating system re-checks that ticket when the app is moved or replaced.
Apple silicon builds compared with Intel builds
Recent releases ship as universal binaries, so one package runs natively on both Apple silicon and Intel processors; older versions may be Intel-only and lean on the translation layer, which works but slows startup and can disturb USB timing. Check which processor your machine uses in the system information panel before comparing versions. A build that predates your operating system release may install cleanly and then fail at the connection stage rather than at launch.
Which owners need the desktop client, and when does a phone app suffice?
Anyone holding a hardware signer who tracks several accounts, runs a node, or approves contract interactions should install the desktop build. A phone application handles single transfers, balance checks and price alerts. The dividing line is not money but complexity: the more accounts, networks and records you inspect, the more a large screen and a real keyboard help.
Portfolio and multi-account work
The desktop layout puts every account linked to one device on a single screen and lets you sort by network, while phone builds show them one at a time. Adding a second account of the same asset usually offers a choice of account index, and that choice is easier to audit with a full keyboard and readable address strings in view. Exporting a transaction history to a file is a desktop-only action in most releases, and the file arrives as comma-separated text.
Custom networks and contract calls
Adding a network that the vendor does not list by default, or interacting with a smart contract, requires the desktop interface in most releases. The signing device still displays a hash rather than decoded contract text on many chains, so you read the parameters in the application window and match them against the screen. That comparison is far harder on a handset, where only one pane is visible at a time.
Device firmware and companion updates
Device firmware is updated through the application, which pulls the signed image and streams it over the cable. A dropped connection midway through a write can leave the signer in a recovery state that has to be reflashed, and the chance of that rises on an unstable link. Wired connections are the more dependable route during a firmware write; Bluetooth is fine during ordinary transfers.
Official builds against mirrors, reuploads and lookalike pages
Only the publisher’s own domain serves the signed, notarized package. Community mirrors, file-sharing reuploads, chat attachments, search advertisements and preinstalled copies all hand you a file whose origin cannot be confirmed. That matters because a modified client can show a different recipient address than the one your signer will eventually approve, and the mismatch is easy to overlook.
The table compares five ways of obtaining the package on an Apple machine against four criteria: what arrives on disk, the main limitation, how strongly you can confirm its origin, and the situations each route suits.
| Route | What arrives | Main limit | Origin check |
|---|---|---|---|
| Publisher’s own site | Notarized disk image signed by the vendor | None beyond trusting your own network | Code signature and notarization ticket |
| Community mirror or reupload | Byte-identical file with no attestation | No chain of custody after upload | Digest compared against the official value |
| Paid search advertisement | Landing page impersonating the vendor | Redirect can change between visits | Hostname spelling and certificate details |
| Chat or email attachment | Package sent by a volunteer or a support account | No verifiable sender identity | None that survives scrutiny |
| Preinstalled on a used computer | Running application with saved account data | Earlier owner may still hold recovery copies | Full erase followed by an independent install |
The first route suits anyone with a working connection and the device at hand, and it is the only route the verification procedure on this page assumes. A mirror suits only the person who already holds a trusted digest from another channel and can compare it. Advertisements and attachments suit nobody: there is no situation where their convenience outweighs the loss of custody. The preinstalled route becomes workable after a full erase and a fresh install taken from the vendor’s own product page.
Why notarization is the check that scales
Notarization attaches a ticket from Apple’s servers to the package, and the operating system validates that ticket at first launch and again after certain replacements. A copied file keeps the ticket, so notarization tells you the archive was signed by a registered developer; it does not tell you that developer is the wallet vendor. The signature’s team identifier is what ties a build to one specific publisher, and that string is the value worth comparing against the one printed on the official page.
What an advertisement placement actually proves
Result pages mix paid placements with organic ones, and a paid slot proves only that somebody bought the keyword. Cloning a product page takes an afternoon: layout, screenshots and wording are copied word for word, and only the domain differs. Certificate warnings rarely appear, because short-lived certificates are cheap. Read the hostname to the left of the first slash, and open the address from a bookmark you created yourself rather than from a result listing.
What breaks after installation and what the software cannot protect
Most failures are environmental: a quarantine flag after a move, a cable that carries power but no data, a background process holding the USB interface, or a system update that resets permissions. None of these are security failures. The real security limit sits elsewhere – a compromised computer can lie about what you see, but it cannot sign without the device.
Quarantine flags and blocked launches
When a package travels between machines through a transfer tool or a removable drive, the system may attach a quarantine attribute that blocks the first launch behind a generic warning. The message names the file rather than the developer, so it reads like a malfunction. Use the package’s context menu and choose Open, or clear the attribute from a terminal window, then re-confirm that the signature is unchanged before you rely on the result.
Cable, hub and port behaviour
Charging cables frequently omit the data lines, so the signer powers on and is never detected. Powered hubs and monitor docks can reorder device enumeration or drop a link midway through a firmware write. Connect the signer straight into a port on the computer, use the cable supplied with the device, and close utilities that claim the same interface, such as backup or phone-management tools.
What a compromised computer can still do
A tampered machine can swap the recipient address shown in the window while the signer displays the true one, so the signer’s screen remains the only dependable reference. It can also delay a broadcast, hide a transaction from your history, or capture account labels and balances – none of which are secrets, but all of which are useful to an attacker. Recovery words never need to touch a keyboard, and any prompt asking you to type them is hostile.
How do you verify an Apple disk image is authentic before opening it?
Pull the disk image from the publisher’s own site, then confirm three things before you double-click: the file’s cryptographic digest matches the published value, the code signature carries the expected team identifier, and the notarization ticket is valid. You need the image file, a terminal window and the official digest listing.
Step 1: Save the file without opening it
Save the file to a local folder without opening it. Launching the installer mounts the volume and triggers first-launch checks before you have compared anything, and an unfamiliar package should sit untouched until its origin is settled.
Step 2: Compare the SHA-256 digest
Compare the SHA-256 hash with the value printed on the vendor’s site. A single flipped byte changes the whole digest, so a mismatch means the file you hold is not the file the publisher signed, no matter how ordinary it looks.
Step 3: Inspect the signature and team identifier
Inspect the code signature and the team identifier. That identifier is the string tying a build to one specific developer account, and matching it against the official page excludes a package signed by an unrelated party.
Step 4: Validate the notarization ticket
Confirm the notarization ticket with the system’s own tool. A valid ticket shows that Apple’s service scanned the build and recorded the developer, while an absent or revoked ticket means the package should not be trusted even if the signature verifies.
Step 5: Mount, copy and eject
Mount the image, drag the bundle across, then eject the volume. Copying rather than running from the mounted disk keeps the application where the system can re-validate it on each launch, and ejecting stops a stale volume from masking a failed copy.
Which details shift between releases and what do owners misread?
Three things move: the minimum operating system version, the list of supported coins and networks, and the connection method the device uses. Version numbers on the application and on the device firmware advance on separate schedules, so a mismatch is normal. Figures such as storage use and asset counts are published on the official source and change without notice.
Minimum system versions and chip support
The minimum operating system version rises whenever the vendor adopts a new framework, and the change often arrives without a visible feature to justify it. An older machine running the previous release keeps working until a server-side change breaks a network integration. Reading the release notes before an update shows whether your machine is still within scope; the current requirement is listed on the official page.
Application version against firmware version
These two numbers are independent: the application may update weekly while firmware sits unchanged, and firmware can be replaced on a device whose companion application is a year old. Update prompts name whichever component has a newer build, and the settings screen lists both strings. When a connection error appears, checking both numbers first avoids a pointless reinstall.
What “keys never leave the device” actually guarantees
That claim is accurate about key material and silent about everything else. Balances, account names, transaction history and the addresses you have used all reach the computer, and a modified client can read them. The guarantee covers signing authority alone: no software on the machine can produce a valid signature without a physical confirmation on the device’s own screen.
Ledger Live Download for Mac Safe User Guide is only as trustworthy as the file it describes, so the first thing to inspect is the signature on the package rather than the version number. Two things decide that: the domain the installer came from and the developer identifier that the Apple operating system validates at first launch. The sections below set out how to confirm both without leaning on a search result, an ad, or a forum mirror.
How the Desktop Wallet Package Reaches an Apple Computer
Distribution runs through a single channel: the maker’s own site, which serves a disk image or an installer package signed with the company’s developer certificate. Apple’s Gatekeeper reads that signature and the notarization ticket at first launch, then refuses anything unsigned. No authentic copy arrives through an aggregator page, a file-sharing link, or a comment thread.
What the Notarization Ticket Confirms
A notarization ticket is Apple’s record that an automated scan of a finished build found no known malicious code. The developer uploads the build, a service scans it, and the resulting ticket can be stapled to the bundle so the check completes without a network request. The ticket says nothing about who wrote the software or whether the address you visited belongs to that author, which is why the developer identifier and the address bar stay part of the same review.
How a Code Signature Binds a Bundle to One Publisher
A code signature is a cryptographic seal that ties every executable inside a bundle to one developer identity. Changing a single byte after signing breaks the seal, and the identifier printed during inspection traces back to a certificate issued through an Apple developer account. Two programs with identical names can therefore carry two different identities, and only the identifier, not the name or the icon, tells you which company assembled the copy on your disk.
Why Catalog Pages Reissue the Same Installer
Third-party catalogs rarely rewrite a program; they wrap it. A stub is placed ahead of the original package, sometimes adding toolbars, browser add-ons, or an extra prompt, while the inner application keeps its valid signature. The signature check therefore passes for the payload although the operator launched the wrapper, which is how a verified inner file ends up carrying unwanted components. The practical consequence: inspect the outermost bundle, since that is what runs first.
Who Needs the Desktop Application, and When Does the Handheld Build Suffice?
The desktop program suits owners who attach a hardware device by cable or Bluetooth, install device-side applications, update firmware, and manage several accounts from one screen. The phone build covers balance checks, transfers, and portfolio review away from a desk. Neither build can move funds without a physical confirmation on the device itself.
Operations That Stall While the Device Is Unplugged
Signing a transaction, sending funds, and editing settings on the device all require the hardware present and unlocked. The program can still display balances and history because addresses and amounts sit on public blockchains, but a private key never leaves the secure element, so a prepared transfer waits until its owner approves it on the device screen. Closing the window in the meantime cancels nothing on-chain.
Read-Only Review That Never Touches the Hardware
Account lists, price charts, and transaction history are read from public chain data, so they refresh with the device disconnected. This makes the handheld build sufficient when the goal is watching a portfolio or checking that a transfer arrived. The limit is symmetric: anything that writes to a chain, from a simple send to a staking operation, needs the hardware unlocked and physically confirmed, and no view in either build changes that boundary.
Older Apple Laptops and the Supported System Release
Every build states a minimum supported release of the Apple operating system, and that floor moves upward over time, so a machine that ran an earlier version may refuse to launch a current one. The same release notes state which processor families are covered. Installing on an unsupported system usually fails at launch rather than with a clear warning, which sends people looking in the wrong place.
Authentic Publisher Site Versus Mirrors, Catalogs, and Shared Files
Only the publisher’s own site pairs the installer with the same developer identifier that signs the device-facing software. Mirrors, catalogs, and shared archives either trail the current release, add a wrapper, or carry nothing to compare against. Which route fits depends on what can be checked and what happens when that check fails.
Five acquisition routes are compared below on three points: who signs the code, how much work the confirmation takes, and where the route breaks down. Version strings, file sizes, and supported system releases shift between builds, so those values are read from the publisher’s page at the time of use rather than carried in memory.
| Route | Who signs the code | Effort to confirm | Where it breaks |
|---|---|---|---|
| Publisher’s own site | The same identity that signs the device software | One Terminal inspection of the bundle | Regional blocking can hide the page |
| Sponsored search placement | An unknown party, often a fresh certificate | Manual address typing ahead of any click | Ads mimic the real site cheaply |
| Software catalog portal | A wrapper, while the inner payload stays signed | Inspecting the outer bundle contents | Bundled extras run alongside the program |
| Open-source package cask | A maintainer, not the manufacturer | Reading the recipe script and checksum | Updates lag, and upkeep can stop |
| Chat or file-sharing archive | Nobody verifiable | Nothing dependable to compare | Recovery-phrase theft cannot be undone |
The authentic page is the only route where a failed check carries information, because a known identifier exists to compare against. An open-source cask fits a scripted setup across many machines, but its maintainer decides when a new build lands and may abandon the recipe; treat the vendor’s page as the reference value. Aggregators and shared archives fit nothing, since an unsigned wrapper leaves no baseline, and the loss of a recovery phrase has no remedy.
Reading the Identifier on a Repackaged File
Repackaging usually leaves the inner program signed and the outer container unsigned. Mounting the image and inspecting the outer bundle returns either an unfamiliar team name or an ad-hoc signature with no authority behind it; comparing that output with the identifier listed in the publisher’s documentation exposes the substitution. A mismatch is a stop signal rather than a warning to weigh, since it shows the container was assembled by a party other than the one named on the page.
Why a Launching Program Can Still Be the Wrong Build
A copy can start, recognize the hardware, and show correct balances while still being the wrong build. The reason is that a doctored interface controls what appears on the computer screen, and a receiving address displayed there can differ from the address the device shows during confirmation. Since the device presents the true destination, reading the hardware screen rather than the monitor is the only check that survives a compromised interface.
Where a Desktop Installation Goes Wrong on Apple Hardware
Three failures repeat often enough to be predictable: a Gatekeeper warning dismissed through a right-click so the program opens anyway, a lookalike address that differs from the genuine one by a hyphen or a single letter, and a request to type the 24-word recovery phrase, which no legitimate process ever makes.
Blocked Launches That Get Overridden
Clearing a Gatekeeper block through the context menu or the privacy settings pane creates a standing exception. That dialog is the only automated judgment that ran on the file, and overriding it converts a stop into an open door: the exception is remembered, so subsequent launches skip the check entirely. Legitimate older utilities sometimes need that route, but a current commercial wallet manager does not, and the presence of the warning is itself the finding.
Addresses That Differ by One Character
A lookalike hostname usually copies the real one and adds a hyphen, a plural, or a different top-level suffix. Paying attention at that moment matters because the copied page is designed to look identical, including its layout and its file names, and the only reliable difference sits in the address bar. Saving the verified page as a bookmark once removes the decision from every later visit.
Requests to Type the Recovery Phrase
The 24 words are shown once, on the hardware screen, during setup, and they reconstruct every account on any compatible device. No web form, support chat, email, or installation step needs them, because signing happens inside the device and never in software. A request to type or photograph them is a theft attempt, and once they are transmitted the outcome cannot be reversed by any later action.
How Do You Verify an Installer’s Authenticity Before Running It?
Confirm three things in order: the address you typed yourself, the version and size published on that page, and the developer identifier that the codesign utility prints on the mounted bundle. Have a browser window, Terminal, and the fetched file ready. The sequence takes a few minutes, needs no account, and can be repeated whenever a new release appears.
Step 1: Reach the Site by Typing Its Address
Open a new browser window and type the publisher’s domain into the address bar instead of clicking a link. A typed address skips redirects, sponsored placements, and shortened links, which are the three routes a lookalike copy uses to reach a machine.
Step 2: Take the File From That Page Alone
Retrieve the installer from that page alone and keep it in a single folder you can find again. Mixing two sources removes the ability to compare, because two files sharing a name almost never share a signature.
Step 3: Record the Published Build Details
Write down the version number, file size, and minimum supported system release shown beside the file. Those three values are the baseline the saved item is measured against, and they change with each release, so they are taken from the page itself.
Step 4: Inspect the Signature in Terminal
Mount the disk image and run the codesign utility against the application bundle inside it. The output names the signing authority and the team identifier, so an absent signature, an ad-hoc label, or an unfamiliar team points to a build that did not come from that publisher.
Step 5: Confirm Notarization and the Device Prompt
Run the spctl assessment tool on the same bundle, then install it and connect the device. Gatekeeper’s verdict reflects the notarization ticket, and after launch every confirmation, including the display of the recovery phrase, should appear on the hardware screen rather than in the window on the computer.
What Stays Unsettled About Notarization Records and Address Changes
Apple’s notarization service keeps no public index of accepted builds, so nobody outside the two parties can confirm a particular version from Apple’s side alone. Hosting arrangements, redirects, and the build a mirror carries change without notice. Values that move are re-read from the publisher’s page at the time of use, not trusted from an earlier session.
No Public Register Links a Build to a Notarization Date
The ticket is checked locally by the operating system rather than listed in a queryable catalog, which leaves two available references: the vendor’s release notes and the signature output on your own machine. Neither is independent of the publisher, and a checksum list is only as current as its last edit. This is a structural limit, not a flaw to work around.
Renamed Paths That Break Saved Bookmarks
Installer paths change between releases, so a bookmark aimed at a specific file can fail while the landing page stays intact. Saving the page rather than the file keeps later visits short and avoids the reflex of accepting whatever a dead link redirects to. Where a release genuinely moved, the redirect target is worth reading prior to reopening anything.
Whether a Published Checksum Is Worth Comparing
A checksum published beside a file confirms that a transfer completed without corruption, and it becomes a real test when the copy being measured came from somewhere else. Comparing the published value against a mirror’s copy catches a swapped build; comparing a value against a file taken from the same page proves only that the transfer worked. The official product page remains the reference point in both cases.
Q&A:
Can I trust the Ledger Live download links that show up in search ads?
Search ads can point to copycat sites. Type ledger.com in the address bar, then go to the download section. The real Mac file is a .dmg named Ledger Live. Check the site certificate and the exact domain before you click. Ledger will not ask for your 24-word recovery phrase during download or setup. If a page asks for it, close the page. For extra safety, bookmark the real download page and use that bookmark next time.
macOS says Ledger Live cannot be opened because Apple cannot check it for malicious software. Is that normal?
This warning often appears for apps outside the Mac App Store. If you downloaded from ledger.com, open System Settings > Privacy & Security. In the Security section, find the message about Ledger Live and click Open Anyway. You may need to enter your Mac password. Another route: open Finder > Applications, right-click Ledger Live, choose Open, then confirm. Do not turn off Gatekeeper for the whole Mac. After it opens once, the warning should stop for that copy. If it keeps appearing, delete the app and download the .dmg again from ledger.com.
How do I check the .dmg file before I install it on my Mac?
Compare the file’s SHA-256 hash with the one published on Ledger’s official download page, if a hash is listed. Open Terminal and run: shasum -a 256 ~/Downloads/LedgerLive.dmg. The output should match exactly. You can also inspect the app’s code signature after installing: codesign -dv –verbose=4 /Applications/Ledger\ Live.app and spctl -a -vv /Applications/Ledger\ Live.app. A genuine Ledger Live app should show a signature from Ledger SAS. If the hash or signature does not match, do not open the file. Delete it and get a fresh copy from ledger.com.
Does Ledger Live need Full Disk Access or other special permissions on macOS?
No. Ledger Live does not need Full Disk Access, Accessibility, Screen Recording, or Input Monitoring. If macOS or the app asks for those, deny the request unless Ledger support has told you otherwise for a specific feature. You may see a Bluetooth prompt when you connect a Ledger Nano X. That permission is for talking to the device. For USB models, you may need to allow the device connection when macOS asks. Keep permissions limited and review them in System Settings > Privacy & Security from time to time.
I downloaded Ledger Live from a site that looked real, and now I am worried. What steps should I take?
Assume the file could be harmful. Disconnect from the internet if you already opened it, move the app to Trash, and empty the Trash. Run a malware scan with a trusted tool. Check your browser for strange extensions and remove anything you do not recognize. Change passwords for exchanges and email, using a different device if possible. Most of all, if you typed your 24-word recovery phrase into any app or web page, treat that wallet as exposed. Create a new wallet with a new recovery phrase and move your funds there. Contact Ledger support through ledger.com only.
How do I download Ledger Live for Mac without getting a fake app?
Type ledger.com/live into your browser and use the link on that page. Do not use search ads, social media links, email links, or downloads from software portals. Pick the macOS version, open the .dmg, and drag Ledger Live into Applications. When you first open it, check that the app name is Ledger Live and that macOS shows it as signed by Ledger SAS. If Ledger lists a SHA-256 checksum for the installer, compare it with the file you downloaded. You can also check the app’s version and release notes on Ledger’s support pages. Ledger Live will never ask for your 24-word recovery phrase on the Mac. It only asks you to confirm actions on the Ledger device. If a Mac app asks for your recovery phrase, close it and delete it. Keep your macOS current and use the official Ledger support site if anything looks wrong.
Why does macOS warn me that Ledger Live cannot be checked for malicious software?
That warning often appears when an app is not from the Mac App Store or when macOS cannot reach Apple’s notarization service. Do not turn off Gatekeeper for all apps. Confirm you downloaded the file from ledger.com/live. If the warning remains, go to System Settings > Privacy & Security, find the message about Ledger Live, and choose Open Anyway. Only do this after verifying the source. Ledger Live will not ask for your recovery phrase. If you are unsure, delete the file and download it again from Ledger’s site.
Ledger Live App iOS: Which handsets run the app and what blocks an install
Research Notice: This guide uses vendor documentation and platform requirements; confirm current details on the official source before acting.
Install Ledger Live App on Your iOS Device starts with confirming the official publisher, checking compatibility, and pairing only after the hardware wallet shows the same code. The mobile companion links a handset to a hardware wallet so balances and approvals can be reviewed on a small screen while private keys remain offline. This article covers what the software does, who it suits, how alternatives compare, common setup risks, and a verification sequence.
What the mobile companion does and how it connects to a hardware wallet
The mobile companion is a bridge between a phone and a hardware wallet: it displays balances, prepares transactions, and relays approvals without exposing private keys. The wallet itself signs, while the phone acts as a screen and network connection. Pairing occurs over an encrypted Bluetooth channel after both sides confirm a code.
Connection through Bluetooth and the vendor’s encrypted channel
Pairing uses Bluetooth Low Energy, which lets the phone and wallet exchange encrypted messages at close range. The companion creates a session key with the hardware wallet, then verifies a short code shown on both screens. If the code differs, the session should be rejected. Range, interference from other wireless hardware, and battery state can interrupt this link, so keep both items near each other during setup.
Account data versus private keys
The companion stores public account data, not the seed phrase or private keys. Public addresses, balances, and transaction history sync from the network so the phone can show portfolio state. Signing rights stay inside the hardware wallet’s secure element. Removing the companion or losing the phone does not move funds, because the seed phrase remains the recovery path.
Firmware and transaction approvals
Transaction approval always happens on the hardware wallet’s screen. The phone prepares a transaction, the wallet displays recipient, amount, and network fee, and the user confirms or rejects on the wallet buttons. Firmware updates may change menu labels or connection behavior, so the companion version and wallet firmware must stay compatible. A mismatch can block signing until one side is updated.
Who benefits from this setup and when a desktop program fits better
Phone-first users who check balances, send small amounts, or approve transactions away from a computer benefit most. The setup suits quick confirmations, travel, and portfolio monitoring without opening a laptop. Desktop software remains better for large transfers, batch actions, detailed account management, and users who prefer a wired connection or a larger screen.
Frequent phone-first users
People who already use a handset for banking, messaging, and two-factor codes often want the same convenience for crypto balances. The mobile companion reduces context switching because the phone handles the network connection while the hardware wallet handles signing. This pattern works well for routine checks and small payments, but it does not remove the need to read every wallet screen before approval.
Travel and quick balance checks
Travel makes a phone the most available screen, and the companion can show balances without exposing keys in a hotel room or airport. The hardware wallet stays in a bag or pocket and connects only when a transaction needs approval. Public wireless networks still carry metadata, so a trusted connection or mobile data is preferable for syncing account activity.
Cases where desktop software remains preferable
Desktop programs handle larger workflows such as many accounts, CSV exports, and firmware management with fewer interruptions. A wired connection can be more stable than Bluetooth in offices with heavy wireless traffic. Users who manage significant sums may prefer to keep signing sessions on a dedicated computer and use the phone only for viewing.
How does the mobile companion compare with desktop, web, and third-party alternatives?
The mobile companion sits between a hardware wallet and online services: it shows balances and prepares transactions, but signing stays on the wallet. Desktop software offers deeper management, web dashboards depend on a browser and vendor session, and third-party trackers often use read-only access. Each route differs in setup effort, custody boundary, and best fit.
The table compares setup path, key custody, and best fit across common routes for managing a hardware wallet from a phone or computer.
| Option | Setup path | Key custody | Best fit |
|---|---|---|---|
| Official mobile companion | Pair over Bluetooth after code check | Keys stay in hardware wallet | Phone-first balance checks and approvals |
| Vendor desktop program | Connect by cable to a computer | Keys stay in hardware wallet | Large transfers and detailed account work |
| Web dashboard | Browser login plus hardware wallet approval | Keys stay in hardware wallet when signing locally | Occasional access from borrowed computers |
| Third-party portfolio tracker | Read-only address import | No signing rights | Viewing multiple wallets in one place |
| Exchange-hosted account | Account signup and identity checks | Exchange controls keys | Trading and custody outsourced to a company |
The official companion fits users who want phone-based signing with a hardware wallet and accept Bluetooth. It does not fit those who need batch account operations or wired stability. Desktop software fits complex management but requires a computer. Web dashboards fit occasional checks if the browser and vendor session are trusted. Third-party trackers fit observation only. Exchange accounts fit trading but move custody to a company, which changes risk entirely.
Official companion versus vendor desktop program
The official companion specializes in quick phone approvals, while the desktop program specializes in depth. The companion’s Bluetooth link is convenient but can drop when the phone moves out of range. The desktop program uses a cable and often exposes more account tools, firmware controls, and export options. Users who sign often should keep both routes available, because a phone-only workflow can become slow when many accounts need attention.
Third-party portfolio trackers and custody boundaries
Third-party trackers usually import public addresses and never receive signing rights. They can combine balances from several hardware wallets, exchanges, and software wallets in one view. That convenience comes with a privacy trade-off: the tracker learns which addresses belong together. A read-only tracker cannot move funds, but it can expose a user’s financial map if the service leaks or sells data.
Risks, limits, and common mistakes during setup
The largest risks are fake listings, rushed pairing, and mishandled recovery phrases. Lookalike software can imitate icons and names while stealing secrets. Bluetooth interruptions can push users to retry carelessly. Storing a seed phrase in photos, notes, or cloud backups creates a permanent exposure that no password can undo.
Fake listings and lookalike publishers
Fake listings often copy artwork but use a publisher name that differs by one word or character. Checking the publisher against the hardware vendor’s official source blocks most of these attempts. Users should also verify the listing’s support link and privacy policy, because a missing or broken policy is a warning sign. If a listing asks for a seed phrase, it is hostile by design.
Bluetooth range and pairing interruptions
Bluetooth pairing can fail when the phone is in a case with metal, the wallet battery is low, or many wireless items crowd the area. Moving both pieces within a few feet and removing interference usually restores the link. Repeated failed attempts can lock the wallet temporarily, so a pause and a fresh code check is safer than rapid retries.
Backup phrase handling mistakes
A recovery phrase must never be typed into the companion, a browser, or a note-taking tool. The hardware wallet shows the phrase once during initial setup, and the user writes it on paper or metal offline. Photographs, cloud notes, and password manager entries create copies that survive deletion. Anyone who obtains the phrase can move funds without the hardware wallet.
How do you verify a mobile companion before pairing a hardware wallet?
Verify the publisher, compatibility, permissions, and pairing code before any transaction. Have the hardware wallet, its recovery phrase stored offline, and the phone’s operating system version ready. This sequence confirms the software source and blocks a nearby unauthorized wallet from joining the session.
Step 1: Open the official source page and locate the current mobile listing.
Open the official source page and locate the current mobile listing. This confirms the publisher before any download.
Step 2: Confirm the publisher name matches the hardware vendor’s published legal entity.
Confirm the publisher name matches the hardware vendor’s published legal entity. Lookalike listings often copy icons but miss the exact publisher.
Step 3: Check the compatibility notes for the phone model and operating system version.
Check the compatibility notes for the phone model and operating system version. Older handsets or unsupported system builds can fail during pairing.
Step 4: Review the permissions requested and disable unnecessary access.
Review the permissions requested and disable unnecessary access. The companion needs Bluetooth and network access, not contacts or photos.
Step 5: Pair only after the hardware wallet screen shows the same connection code as the phone.
Pair only after the hardware wallet screen shows the same connection code as the phone. A matching code blocks an unrelated nearby wallet from joining the session.
What changes over time and what people commonly get wrong
Version requirements, regional availability, and support articles shift as vendors update software and regulations. A setup that worked last year can fail after an operating system release or a firmware change. Users often assume a phone backup protects crypto, or that a read-only tracker can sign, or that Bluetooth pairing equals ownership.
Operating system and firmware version requirements
Apple’s mobile platform and the hardware wallet firmware both receive updates that can change connection behavior. The companion may require a minimum operating system version, and the wallet may require a minimum firmware release. Checking the official source before updating avoids a mismatch where the phone sees the wallet but cannot sign. Older phones may stop receiving support entirely.
Regional availability and account types
Some features depend on region, account type, or local rules. Exchange connections, buy services, and staking options can appear in one country and not another. A user with a self-custody hardware wallet may see different menu items than a user with only a software account. The official source publishes current coverage, so local assumptions should be checked there.
Support articles and release notes as moving targets
Support articles and release notes change without notice when vendors patch bugs or rename menus. A screenshot from a blog post may show an older layout that no longer matches the current version. Reading the release notes for the companion and wallet firmware before troubleshooting saves time. If a step in an old guide does not match the screen, stop and confirm the flow on the official source.
Research Notice: This article explains compatibility checks using publicly documented requirements. Manufacturer support lists and system thresholds can change; confirm current details on the official source before acting.
Install Ledger Live App on Your iOS Device starts with a compatibility audit, not a download. The official companion tool demands specific tablet system and phone firmware versions, along with enough free space for blockchain data. Skipping this check leads to crashes, pairing failures, or an unusable wallet dashboard.
Check iPhone and iPad Compatibility with Ledger Live Before Installation
Confirm the handset model, operating system version, and free storage before loading the wallet companion. The current client requires tablet system or phone firmware within a supported range, plus at least 200 MB of free space for basic operation. Older units with limited memory may pair but fail during account synchronization.
Operating system version thresholds
The companion suite refuses to launch on firmware older than the vendor’s published minimum. For Apple phones, that floor usually matches the last two major system releases. Tablets need the equivalent tablet system build. When the firmware falls below that line, the program shows an incompatibility warning before any account data loads. Checking the version takes ten seconds in Settings > General > About.
Available storage and memory demands
At least 200 MB of free space is needed for the initial setup and blockchain caches. Heavier account histories can push that figure higher. Handsets with 16 GB total capacity often run out of room after system updates. The wallet manager performs best with 2 GB of RAM or more. Insufficient memory causes the interface to freeze during address generation.
Bluetooth and secure element constraints
Wireless pairing relies on Bluetooth Low Energy, available on iPhone 4S and later, plus iPad 3 and newer. The secure element inside the hardware wallet handles signing keys, not the phone itself. A handset without a modern Bluetooth stack can still connect via cable on some models, but cable support is limited. Check the manufacturer’s accessory list for exact cable compatibility.
Which iPhone and iPad models run the official wallet companion smoothly?
Recent iPhone and iPad models with at least 2 GB of RAM and a current system build run the companion without stutter. The iPhone 8 and later, plus iPad Air 3 and iPad 6th generation, meet the typical baseline. Older units may launch the program but drop connections during firmware updates.
iPhone models from 2017 onward
Apple phones released from 2017 forward generally include the memory and Bluetooth profile required for stable pairing. The iPhone 8, X, XR, and all later series handle account synchronization without repeated timeouts. The iPhone 7 can work for basic viewing but may fail during multi-account signing. Check the official support page for the latest confirmed list.
iPad tablets with sufficient headroom
iPad tablets need the same memory floor, but their larger screens do not change the underlying requirements. iPad 6th generation, iPad Air 3, and iPad Pro 2018 or newer are commonly cited. Older iPads with 1 GB of RAM often crash when loading transaction history. The tablet’s storage must also have 200 MB free after system updates.
When a handset is too old for reliable signing
A phone that meets the launch minimum but lacks a secure enclave or modern Bluetooth may pair yet fail at the signing step. Such units can display balances but cannot approve transactions. The companion will show an error after the hardware wallet challenges the handset. In that case, use a desktop computer or a newer tablet instead.
How does the wallet companion compare with browser-based dashboards?
The official companion offers native Bluetooth pairing and local encryption, while browser-based dashboards run inside Safari and rely on WebUSB or WebBLE. A third-party portfolio tracker reads public addresses only. The companion remains the only option for firmware updates and secure transaction signing on Apple phones and tablets.
The comparison below weighs three access routes for managing a hardware wallet from Apple hardware. Criteria include how each method handles signing, its main limit, setup effort, and how to verify compatibility.
| Route | Best for | Main limit | Verification |
|---|---|---|---|
| Official companion | Full account control and firmware updates | Needs recent tablet or phone system | Check official model list |
| Browser-based dashboard | Quick balance checks on a borrowed computer | No native Bluetooth pairing on some tablets | Confirm browser and cable support |
| Third-party portfolio tracker | Read-only history and tax reports | Cannot sign or update firmware | Verify address import method |
| Desktop program | Firmware updates and large screen review | Requires a computer with a cable | Check desktop system requirements |
The official companion fits users who need to move funds or update firmware. Browser dashboards suit temporary balance checks when native pairing fails. Third-party trackers work for accounting but cannot authorize transactions. Exceptions exist: some newer iPads support WebBLE, blurring the line between native and browser routes.
Native Bluetooth versus browser bridge
Native pairing uses the tablet’s own Bluetooth stack, which the companion controls directly. Browser bridges pass data through Safari’s WebBLE API, adding a permission prompt and occasional timeouts. For firmware updates, only native pairing is permitted because the process requires a stable, encrypted channel. A browser bridge may drop the connection mid-update, leaving the hardware wallet in recovery mode.
Read-only trackers and their limits
Read-only trackers import public addresses and show balances without any signing ability. They cannot update firmware, approve transactions, or access private keys. This makes them safe for monitoring but useless for moving assets. A user who needs to send funds must switch to the official companion or a desktop program. Verify that the tracker never asks for a seed phrase.
What limits appear when older handsets or low storage are used?
Older handsets often launch the companion but fail during account synchronization, firmware updates, or Bluetooth reconnection. Low free storage below 200 MB blocks the initial database build. Units with 1 GB of RAM may freeze when generating receiving addresses. These limits are hard stops, not slowdowns.
Storage exhaustion during blockchain sync
The companion builds a local cache of account histories, which grows with each added wallet. A phone with less than 200 MB free cannot complete that build. The program may loop on a loading screen or quit unexpectedly. Freeing space by deleting photos or other applications can resolve the issue temporarily. Long-term use needs at least 500 MB of headroom.
Outdated firmware blocks secure enclave access
Apple’s system software mediates access to the secure enclave, which stores biometric permissions. When the firmware falls below the companion’s minimum, that bridge is disabled. The program then refuses to sign transactions even if Bluetooth pairing succeeds. Updating the phone firmware is the only fix, but some older models cannot receive the required build.
Bluetooth pairing failures on older iPads
Older iPads use Bluetooth 4.0, while newer hardware wallets prefer Bluetooth 5.0 for faster handshakes. The connection may still form, but it drops during multi-step operations. Symptoms include repeated pairing requests and a spinning progress indicator. A wired connection via a camera adapter can bypass the issue on supported tablets.
How to verify handset compatibility before adding the software?
Verification means checking three items: the operating system build, free storage, and the model’s appearance on the official support list. Have the phone or tablet nearby and open Settings. This procedure takes about two minutes and prevents failed setups, data loss, or a locked hardware wallet.
Step 1: Open Settings and note the firmware version.
Open Settings, tap General, then About, and write down the software version. This number determines whether the companion will launch at all, because the program enforces a minimum build.
Step 2: Check free storage in the same menu.
Return to General, tap iPad Storage or iPhone Storage, and confirm at least 200 MB free. The program needs that space for its initial database, and a full drive causes an immediate crash.
Step 3: Confirm the model name against the official list.
Look up the exact model identifier on the manufacturer’s compatibility page. Marketing names like iPhone 8 can hide regional variants that lack required Bluetooth profiles.
Step 4: Test Bluetooth with a known accessory.
Pair a Bluetooth headset or speaker to confirm the radio works. A failed pairing with any accessory indicates a hardware fault that will also block wallet communication.
Step 5: Review the secure enclave status in Settings.
Navigate to Face ID & Passcode or Touch ID & Passcode and verify biometrics are enrolled. The companion uses that secure path for transaction approval, and missing enrollment blocks signing.
Which compatibility details shift with tablet system and watch updates?
Apple’s annual system updates can raise the minimum firmware floor, add new Bluetooth requirements, or change background execution rules. The manufacturer publishes updated compatibility lists after each major release. A handset that worked last year may fall below the new threshold. Check the official source before every major system upgrade.
Minimum tablet system version changes without notice
The companion’s minimum tablet system build is set by the manufacturer, not by Apple. A point release like 16.4 can become the new floor if security patches affect Bluetooth. Users who delay updates may find the program refuses to connect. The official support page lists the current floor, and it can change mid-year.
Model support lists are updated quarterly
Hardware wallet vendors retire support for older phones and tablets as testing resources shrink. A model that appears today may be removed from the confirmed list in three months. The removal does not brick the hardware wallet, but the companion may stop pairing. Users should archive the support page or subscribe to release notes.
Region-specific features depend on local rules
Some regions restrict Bluetooth pairing for financial tools or require additional encryption. The companion may disable wireless signing in those areas while keeping cable support. Apple’s regional firmware builds can also omit certain Bluetooth profiles. Check the manufacturer’s regional notice on the official source before relying on wireless operation.
Q&A:
Can I use Ledger Live on my iPhone with any Ledger hardware wallet?
Not with every model. The iOS app connects to a hardware wallet over Bluetooth. Ledger Nano X, Ledger Stax, and Ledger Flex support Bluetooth. Ledger Nano S and Nano S Plus do not, so they cannot pair with an iPhone through Ledger Live. You can still use those models with Ledger Live on a computer and a USB cable. If you own a Nano S or Nano S Plus, the iPhone app can be installed, but it won’t be able to manage accounts on that device.
Which iOS version does Ledger Live need?
The App Store listing shows the exact iOS version required. At the time of writing, many versions need iOS 13.0 or later. That can change, so check the App Store page on your iPhone or iPad before installing. If your device cannot update to the required version, the app will not appear as compatible or will not install. For older iPhones, use Ledger Live on a supported computer instead.
I searched the App Store but cannot find Ledger Live. What now?
Search for “Ledger Live” and check the developer name. The official app is published by Ledger SAS. If it does not appear, your App Store region may not offer it, or your iPhone may not meet the iOS version requirement. Do not install a random app with a similar name. Also avoid downloading an .ipa file from a website; that can expose your recovery phrase or funds. If the app is unavailable, use the desktop version from Ledger’s website.
How do I pair my Ledger Nano X with the iPhone app?
Install Ledger Live from the App Store, open it, and choose the option to connect a device. Turn on Bluetooth on the iPhone and on the Ledger Nano X. Unlock the Nano X with your PIN. On the device, open the Bluetooth menu and select Pair. The app should show a code; confirm it on the Ledger screen. If pairing fails, turn Bluetooth off and on, restart the Ledger, and make sure the firmware is up to date. You may need to update firmware with Ledger Live on a computer first.
Can I restore my accounts in Ledger Live on iOS without the hardware wallet?
No, not for spending or verifying addresses. Ledger Live is a companion app; your private keys stay on the Ledger device. On iOS, you can install the app and add accounts only when the compatible Ledger device is connected and unlocked. If you only want to view balances, you might use a watch-only setup for some accounts, but that depends on the app version and account type. Never enter your 24-word recovery phrase into the iPhone app or any website.
Can I install Ledger Live on my iPhone before I have my Ledger hardware wallet?
Yes. You can download Ledger Live from the App Store and open it without a device connected. The app will show setup steps, but you can skip device pairing until your Ledger arrives. To install, open the App Store, search for “Ledger Live,” check that the developer is Ledger SAS, and tap Get. After installation, create a password or use Face ID for app access. When your hardware wallet arrives, connect it via Bluetooth or cable, then add accounts. Keep your recovery phrase written on paper and stored offline. Never type it into the app or any website. If you buy a used device, reset it first and set a new PIN.
Why can’t I find Ledger Live in the App Store on my iPhone?
Several reasons can cause this. Your iPhone may run an iOS version below the app’s minimum requirement. Check Settings > General > About to see your iOS version, then update if possible. Another common cause is the App Store region linked to your Apple ID. Ledger Live may not be listed in some countries or regions due to local rules. You can check your Apple ID region in Settings > [your name] > Media & Purchases > View Account > Country/Region. Changing regions is not a quick fix; it can affect subscriptions, payment methods, and store credit. Do not download Ledger Live from third-party sites, sideload it, or use a modified App Store. Those methods can expose your device and funds to malware. If the app is still missing, contact Ledger Support through the official website and ask about availability for your country.
How should I update Ledger Live on iOS without risking my crypto?
Open the App Store, tap your profile picture, and pull down to refresh the updates list. Find Ledger Live and tap Update. You can also turn on automatic app updates in Settings > App Store. Updating Ledger Live does not require your recovery phrase, so never enter it during an update. The app only needs your device PIN, Face ID, or Touch ID to open. Before any update, confirm your recovery phrase is still written down correctly and stored offline. After the update, open Ledger Live and check that your accounts and balances appear as expected. If the update fails, restart your iPhone, free up storage, and try again. If the App Store shows an error, sign out of your Apple ID and sign back in, or contact Apple Support. Do not delete the app as a first step; deleting it does not delete your crypto, but you may need to add accounts again. If you see a request for your 24-word recovery phrase inside the app or on a website, stop. That is a scam.
On November 24, 2025, the 19th EAS Cafè was organized to discuss the relevance of soft skills for the employability of athletes at the end of their sport career and to raise the awareness of the educational platform for young athletes (https://SS4DC.eu) now available thank to the collaborative efforts of the ERASMUS+Sport SmartStart4DC consortium (101133555).
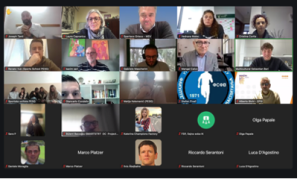
Prof. Cristina Cortis (University of Cassino and Lazio Meridionale, Italy) welcomed around 100 participants and moderated the interesting questions addressed at the endo of the speakers’ presentations.
The Cafè was opened by Mrs. Vedrana Malec who illustrated how her outstanding athletic cross-country skiing helped her improving different soft skills, which are extremely useful for her professional careers, followed by Mr. Sebastian Harry Lloy Algie, who highlighted how soft skills helped him as a basketball athlete in different contexts and a student in physiotherapy, and by Mr. Joseph Tanti who shared his experience as an elite handball athlete in countries with different sport cultures and as a coach of youth teams in Malta. These testimonies stimulated a participated discussion on the important role of soft skills, which are usually lacking in formal educational paths.
To enhance the student-athlete knowledge, competences, and skills, Mr. Renato Vuk, coordinator of the Smart Start for DC, illustrated the SS4DC platform encompassing educational material organized in 10 modules regarding Communication Skills, Social interaction skills, Emotional Intelligence, Listening skills, Leadership, Team-work and Collaboration, Time Management, Desire for Continuous Learning, Critical Thinking, and Respect for Diversity. Whilst the educational course for athletes encompasses videos, text lessons, reflections, and self-assessment tests for each module, the section dedicated to the educators presents manuals and presentations in several languages (e.g., English, Bulgarian, Croatian, Greek, Italian, and Turkish). Furthermore, the platform offers self-assessments for career guidance in sports, labour market, continuing education, and transferable skills. Finally, Mr. Vuk invited the participants to follow the social media of the SS4DC project.
A special thank to mr. Marco Pinchera who translated the speeches in visual-gestural language for the deaf community.
Ledger Live iOS Setup: Installation Routes Compared, from Store to Lookalike
Ledger Live iOS Setup and Security Guide: install the client only from the App Store listing that the vendor’s own site links to, pair it over Bluetooth with a Nano X, Stax or Flex, confirm every destination address on the device screen, then keep the 24-word recovery phrase off the phone entirely. Nothing else on this page matters as much as those four habits, because the handset is the least trusted link in the chain. What follows covers how the wireless link carries data, which installation routes exist, where each one fails, a five-step authenticity check, plus the details that move with every release.
How the iPhone client talks to a hardware signer
The mobile client stores no private keys. It assembles a transaction, encodes it, pushes it across an encrypted Bluetooth or USB link, and waits for a signature. The hardware signer decodes the payload, displays the destination and amount on its own screen, and signs only after a physical button press.
A companion client, in this context, is any program that reads public addresses and builds unsigned transactions while holding none of the material needed to sign them. The signer is the only component that holds that material, which is why every confirmation that matters happens on its screen rather than the handset’s.
Private keys never leave the secure element
A secure element is a tamper-resistant chip that stores the seed and performs the elliptic-curve signing operation internally. The phone receives the resulting signature, never the key. That split explains why a compromised handset can drain nothing on its own: an attacker who controls the operating system can alter the address it displays, but the signed payload still has to be approved on the device screen. The trade-off is a slower confirmation flow, one button press per transaction, which is the price of keeping the seed isolated.
Wireless pairing is limited to certain hardware revisions
A Bluetooth radio exists only on the Nano X, Stax and Flex lines; the Nano S and Nano S Plus are wired-only, so they cannot pair with a phone at all. Owners of those two models must run the desktop client on a computer. Firmware channel, model revision and application release all gate the pairing screen, so a missing device option usually means the model lacks the radio rather than that the software is broken. Current support lists are published on the vendor’s official application page.
What the encrypted link does not prove
Pairing establishes an encrypted channel and a shared six-digit code, which stops a nearby device from impersonating the signer during that session. It says nothing about whether the address rendered on the handset matches the address inside the payload. Malware on the phone can swap a clipboard address or redraw a screen. The only check that survives that attack is reading the destination and amount on the signer’s own display before approving. Treat the handset screen as a convenience view, not as evidence.
Who should run the mobile client, and when is the desktop build a better fit?
The mobile build fits anyone who signs while travelling, at a till, or away from a desk, provided the signer has a Bluetooth radio. The desktop build fits wired-only models, large batch operations, and users who prefer a keyboard for entering addresses. Neither build changes what the signer approves.
Signing away from a desk
Portable signing covers the case where a holder needs to move funds during a trip, accept payment at a market stall, or approve a transaction while the computer is elsewhere. The handset supplies the network connection and the interface; the signer supplies the approval. Because the transaction is built on a device that may run modified software, the device-screen check matters more here than on a desktop, not less. Bluetooth range and battery state are the practical limits.
Holders running several accounts at once
The mobile client can track multiple accounts across several chains and shows balances read from public explorers or the vendor’s indexers. It cannot sign for a wired-only signer, and it cannot perform operations that need a full node, such as some staking or contract interactions. Accounts remain on-chain objects; deleting the application removes the local view, not the funds, and restoring that view requires the signer to be present.
Shared, managed, or borrowed computers
On a machine that an employer administers, endpoint agents can capture keystrokes, screenshots and clipboard contents. The signer still protects the keys, but address substitution and clipboard hijacking become realistic. The mobile build does not remove that class of risk; it moves it to a handset that may carry fewer monitoring agents. Where neither device is trusted, the signer’s screen remains the single reliable display.
Installation routes compared: store build, desktop build, third-party wallet, lookalike
The App Store build suits phone-first signing on Bluetooth-capable models. The desktop build is the only route for wired-only signers. Third-party wallets let the same signer serve chains the companion client does not list, at the cost of a second interface. A lookalike from a search result or an advertisement is never a route; it exists to collect recovery phrases.
Four routes put a transaction in front of the same signer. They differ in which models they accept, what the interface can see, and how a user can tell an authentic build from a copy. The criteria below are model support, main limit, and the check that catches a fake.
| Route | Best for | Main limit | Authenticity check |
|---|---|---|---|
| Store build from the vendor’s link | phone-first signing on wireless models | needs a Bluetooth-capable signer | listing reached from the official site |
| Desktop client | wired-only signers, batch entry | tied to one computer | installer signature published on the official source |
| Third-party wallet paired to the signer | chains the companion client omits | second interface, its own backup duties | read the request on the device screen |
| Browser-extension wallet | desktop contract work | exposes the browser session | device screen shows the final payload |
| Lookalike from search or ads | nothing; it is a collection channel | harvests the recovery phrase | none; treat it as hostile |
Each route fits a situation and fails outside it. The store build fails on a Nano S or Nano S Plus because there is no radio to pair. The desktop client fails for a holder who travels without a laptop. A third-party wallet fits when the chain is not listed in the companion client, and fails when its own interface lags behind the signer’s firmware. Exceptions cluster around hybrid setups: a user may keep the desktop client for firmware work and the phone for daily approvals.
Why a store listing is not proof of authenticity
App review checks that a submission follows platform rules; it does not confirm that the publisher is the company that built the signer. Clones have appeared under near-identical names and icons. The check that works is the path: open the vendor’s own site, follow its link to the listing, then compare the developer name and the version number with the release notes. If the listing cannot be reached that way, treat the build as unverified regardless of its download count or ratings.
What a third-party wallet sees and what it never sees
An alternative wallet reads addresses and balances through its own node or an indexer it chooses, so the provider learns which accounts a user tracks. It builds transactions and hands them to the signer, then relays the signature. It never receives the seed, because the signing operation happens inside the secure element. The consequence is a split trust model: the interface can mislead, the signer cannot be forced to approve, and the device screen stays the deciding view.
Where installations and pairings fail: risks, limits, mistakes
The failures that cost money are few and predictable. A recovery phrase typed into anything digital is exposed permanently. A wireless firmware update interrupted mid-write can leave the signer in a bootloader state. Impersonated support staff asking for the phrase in chat are the most common social route to a drained account.
A recovery phrase typed anywhere is exposed permanently
Twenty-four words, once entered into a website, a chat window, a photograph or a password manager, exist outside the signer for good. An attacker holding those words restores the same accounts on any compatible device and signs without the original hardware, and no vendor, exchange or support agent can reverse the transfer. The rule is mechanical: the words are written on paper or metal at initialization and read only by the signer itself. Any prompt that asks for them is hostile by definition.
Interrupted wireless updates and battery state
A firmware write is a single uninterrupted operation. If the Bluetooth link drops or the signer’s battery dies mid-write, the device can restart into a bootloader screen that no phone can recover. Updates over a cable, with the signer charged and the client closed to other sessions, avoid the failure. A signer stuck in that state may need vendor-assisted recovery; whether a given model can be recovered this way is published on the official source.
Impersonated support and phishing pages
Search advertisements, direct messages and cloned help sites all copy the vendor’s branding and ask for the twenty-four words under the pretext of a sync, migration or validation. No legitimate process needs them, on any device, at any time. The check is structural: support never initiates contact, and the only place a phrase is ever read is the signer’s own screen during a restore. Treat an unsolicited link as a hostile artifact rather than a convenience.
How do you confirm an iPhone install is genuine before pairing?
The procedure verifies that the application on the handset came from the company that built the signer, before any account data or device pairing is involved. Have ready: the signer itself, its screen, a browser, and the vendor’s official site open on a second device or tab.
Step 1: Open the vendor’s own site and follow its link to the app listing
Open the vendor’s own site and follow its link to the application listing. A search result or a sponsored placement can point at a copy that carries the same name and icon, and the path from the official domain is the only one that closes that gap.
Step 2: Compare the developer name on the listing with the company that made your signer
Compare the developer name on the listing with the company that made your signer. Publishers can register similar names, so a match is a filter rather than a guarantee, while a mismatch is a reason to stop immediately.
Step 3: Check the listed version against the release notes on the official site
Check the listed version against the release notes on the official site. A build that lags many releases behind, or that has no matching notes, is more likely an abandoned clone than a current product.
Step 4: Install the build and review the permissions it requests
Install the build and review the permissions it requests before connecting anything. A genuine build asks for Bluetooth, network access and, at most, camera access for QR scanning; requests for contacts, messages or accessibility control do not belong in this class of tool.
Step 5: Pair the signer and confirm the code on both screens
Pair the signer and confirm that the code displayed on the handset matches the code on the signer’s screen. That comparison binds the two radios for the session; afterwards, every destination address is read on the signer’s display before approval, because the handset view can be altered.
Release drift: model support, regional availability, and services that change terms
Three things move after publication: which hardware revisions carry a wireless radio, which regional storefronts carry the application, and what optional recovery services cost or cover. None of them can be inferred from an older article. Each is published on the official source and should be re-checked before a purchase or a restore.
Model support and firmware channels shift with each release
New signer revisions arrive with different radios, screens and firmware channels, and older models are eventually dropped from active development. A support matrix that was accurate a year ago may list a model that no longer pairs, or omit one that does. The practical consequence is that a buyer should confirm the current compatibility list before paying, and a holder should confirm it before assuming a pairing failure is a software bug.
Regional storefronts and optional recovery subscriptions
Storefront availability differs by country, and an application listed in one region may be absent or restricted in another. Optional recovery subscriptions that store encrypted shares of the seed with identity verification also vary by jurisdiction, and their terms, coverage and pricing change. Whether a given subscription applies to a given model, and what it costs, is published on the official source rather than fixed here. Read the terms before enrolling, because enrolment changes who can help recover an account.
How to Install Ledger Live on iPhone from the App Store needs three things before you tap anything: a signed-in Apple ID, a handset running a supported version of Apple’s mobile operating system, plus free space for a small client. The download is the easy part. What decides whether your holdings stay put is the developer field on the listing, the code shown on the hardware screen during pairing, plus the version string you keep after every update.
How the Handset Client Talks to the Hardware Unit
The phone build is a screen, not a vault. It reads public balances, assembles unsigned transactions, passes them to the hardware unit for approval, then broadcasts whatever returns signed. Your recovery words stay inside the signing device throughout, so a lost handset exposes cached addresses rather than the keys behind them.
Keys Remain Inside the Signing Device
A phrase generated on the hardware unit never travels to the handset, which is why a phone can be replaced without moving holdings. The client requests public addresses only; each address is derived from the seed stored inside a dedicated chip built to resist extraction. Pairing authorises a conversation, not a copy. Removing the app therefore deletes a viewer, while the seed survives in the device until you deliberately restore it elsewhere.
What the Phone Keeps After Installation
The handset stores account labels, cached balances, one pairing record per hardware unit, plus your display preferences. None of that is needed to recover anything, so wiping the app costs convenience rather than access. The pairing record matters most: it holds the identifier the device expects, which is why a reinstall usually asks you to confirm the link on the hardware unit again. Balances refresh while the app is open, since the client queries public nodes on demand instead of holding a copy of any chain.
Why the Device Screen Outranks the Phone Screen
An address rendered on a phone can be swapped by malware before you copy it; the hardware display is the reference point. The client therefore asks you to compare the receiving address on the device against the one shown on the handset before approving. Treat any mismatch as a stop signal rather than a glitch. That comparison is the step which makes a compromised handset survivable.
Who Gets Value From the Phone Build, When It Applies, When It Does Not
Install it if you already own the signing device, check balances more often than once a month, or want approvals away from a desk. It adds little for someone holding one long-term position who rarely signs, or for anyone who has not yet bought the hardware unit, since the client does nothing without one.
Frequent Checkers With a Paired Device
Someone who moves assets weekly notices the difference at once: pending confirmations, fee estimates, plus a history view appear without opening a laptop. The pairing survives restarts, so a quick approval takes under a minute. The trade-off is exposure, because a phone travels, gets unlocked in public, sits on shared chargers. Keep the app behind a device passcode plus a biometric lock, both of which the client offers in its own settings.
Long-Term Holders Who Rarely Sign
For a position touched twice a year, the mobile client largely duplicates the desktop build. Installing it costs nothing, yet every extra viewing surface is another place where a phishing link can be tapped. If you sign rarely, keep the phone build installed but unpaired, or skip it, then move the occasional transfer to a machine you control. Convenience is the only loss.
People Who Do Not Own the Signing Device Yet
The application cannot create a hardware-backed seed, so installing it before the physical unit arrives leaves a viewer with nothing to view. A listing promising phrase generation inside the phone app is either a different product or an impostor. Obtain the device from the vendor’s own store first, then install the client. Sequencing this way also means your first pairing happens while you are paying full attention.
Distribution Channels Compared: Store Listing, Desktop Build, Clones
The store listing is the one channel that updates through Apple’s review pipeline; the desktop build updates through the vendor’s own installer, while clones never update honestly at all. Which fits depends on where you sign: a phone-first user wants the store build, a desk-bound user wants the desktop client, nobody wants a clone.
The table compares four channels by what arrives, the main limit each imposes, plus the route for confirming authenticity on the vendor’s official download page. Those criteria decide whether an update can quietly change behaviour: delivery path, developer identity, version transparency, hardware pairing support.
| Channel | What arrives | Main limit | Verification route |
|---|---|---|---|
| Apple store release | Signed build delivered through the platform’s review pipeline | Needs a handset on a supported system version | Developer field matches the vendor’s download page |
| Google Play build | Same client compiled for Android handsets | Different platform, separate pairing prompts | Same developer check inside that store |
| Desktop installer | Full client for macOS, Windows, Linux | A computer is needed for each signing session | Published hash beside the download |
| Look-alike listing | Unknown binary carrying a similar icon | No vendor support, no seed protection | Absent from the vendor’s download page |
Reach for the store release when the phone is your main signing surface plus you want updates handled for you. The desktop installer suits anyone keeping a dedicated machine, since a published hash can be checked before launch. Neither fits a shared or borrowed handset, where someone else can install a clone without your knowledge. Where a device is old enough to fall outside supported versions, the vendor’s page states the minimum, plus anything absent from it stays unverified.
Why Update Delivery Changes the Risk
An update replaces the code you already trusted, so the delivery path matters more than the first install. Store builds arrive signed by a developer identity the platform verified, so a third party cannot push one. A desktop installer depends on you checking a published hash before running it. A clone updates whenever its operator chooses, often adding a screen that asks for your recovery words. That request alone identifies it, because the genuine client never needs those words.
The Naming Trap in Look-Alike Listings
Clones rarely copy the vendor’s name exactly; they add a suffix, swap a letter, or lean on a word that reads as official. The reliable test is the developer field on the listing, compared against the download page the vendor publishes. A second test is the permission list: an app requesting contact access or message reading has no reason to exist in this category. Report such a listing instead of rating it, since removal protects the next person.
Failure Points: Clones, Stale Builds, Misread Prompts
Most bad outcomes trace to three causes: a listing that was never the vendor’s, a build too old to pair with newer firmware, or a prompt approved without reading the address on the hardware screen. Each has a cheap check. None of them involves recovery words, which no genuine prompt requests.
Pairing Failures From Version Mismatch
The handset client plus the device firmware negotiate a protocol at pairing time; when one side sits several releases behind, the link drops after the code comparison. The fix is unglamorous: refresh the firmware through the desktop client, update the phone app from the store, then pair again. Wireless interference explains a smaller share of failures, so step away from crowded airwaves before assuming a version problem. Support pages list the combinations the vendor tests.
Blind Approval of Transaction Prompts
A prompt approved without reading is a signature handed over. Malware on a handset can rewrite the recipient address in the app’s display, which is why the hardware screen is the only trustworthy source. Slow down on two fields: destination address plus amount. If the screens disagree, reject on the device, then reinstall from the store listing. A broadcast transaction cannot be recalled, so no support desk can reverse it.
Treating a Phrase Request as Routine
No genuine installation, update, or pairing flow asks for your recovery words. A screen requesting them, however official it looks, is harvesting. The same holds for unsolicited support messages offering to validate a wallet. Treat any such request as proof the channel is hostile, close it, then look up the real procedure on the vendor’s own site.
How Do You Confirm the Installed App Is Genuine?
Verification takes five checks plus about ten minutes, and it needs the vendor’s download page open beside the phone. You will compare the developer name, the version string, the pairing code, plus the listing’s stability after an update. Nothing in this procedure requires typing a recovery phrase.
Step 1: Open the source page, not a search result
Open the vendor’s download page directly, then follow its link to the store listing. Search results can place a paid advertisement above the genuine entry, so the vendor’s own page is the safer starting point.
Step 2: Compare the developer field
Compare the developer name on the listing against the name published on that download page. A close spelling variant is the usual tell, since exact-name impersonation is harder to keep live.
Step 3: Match the version string to release notes
Read the version string inside the app’s settings screen, then match it to the release notes on the vendor’s site. Release notes carry the numbers that matter, while blog posts often lag behind them.
Step 4: Check the pairing code on both screens
Pair the hardware unit once, then check that the code shown on both screens is identical. A mismatch means the conversation is not with your device, so cancel instead of approving.
Step 5: Re-verify after every update
Re-check the developer field after the next update lands, then note the version you are running. An update is the moment a listing can change hands, so the check costs seconds at the point of highest risk.
What Goes Stale in This Installation Over Time?
Three things move: the minimum handset operating-system version the client accepts, the firmware releases the pairing protocol tolerates, plus the hardware models the vendor still supports. Each is published on the official source rather than fixed here, because they change with every release cycle. Check them before relying on an old phone.
Minimum Handset Versions Rise With Each Major Release
Apple’s mobile operating system gains a version each autumn, plus the client usually follows within a few months. A handset stuck two or three releases behind eventually stops receiving store updates, which is when pairing errors start. The vendor’s listing states the minimum it accepts, so read that line before assuming an older phone is fine. Keeping the handset updated is cheaper than replacing a device that merely fell behind.
Firmware Compatibility Is a Moving Pair
The phone client plus the device firmware must agree on a protocol, so an app update can temporarily outpace a device that has not been refreshed. Desktop clients usually carry the firmware update path, which means a phone-only user may need a computer occasionally. Check the support pages for the combinations the vendor tests; guessing here produces dropped pairings that look like hardware faults.
Support Windows for Older Hardware Models
Hardware generations retire at different times, plus a model that still signs can lose new features first. When a device falls outside the supported list, the phone client may still connect for basic transfers while newer account types stop appearing. The vendor’s compatibility table is the only place that settles this, since resellers keep listing discontinued units. Choose against the supported list rather than the discount.
Q&A:
Can I set up Ledger Live on my iPhone with a Ledger Nano S Plus?
No. The iPhone version of Ledger Live talks to hardware wallets over Bluetooth. The Ledger Nano S Plus uses USB only, so it will not pair with an iPhone. You need a Bluetooth-capable Ledger model, such as Nano X, Stax, or Flex. If you own a Nano S Plus, use Ledger Live on a computer with a USB cable. The iOS app will not detect it.
Does Ledger Live ever ask for my 24-word recovery phrase during iOS setup?
No. During setup, Ledger Live asks you to connect your Ledger device, enter its PIN on the device, and follow the prompts shown on its screen. If you are restoring a wallet, you type the recovery phrase directly on the hardware wallet, not in the app. Ledger Live never needs your phrase. Any app, website, email, or person asking for your 24 words is trying to steal your funds. Keep the phrase offline and never type it into a phone, computer, or browser.
Which iOS security settings should I turn on after installing Ledger Live?
Use a strong iPhone passcode, enable Face ID or Touch ID for Ledger Live, and set the screen to lock right away. Turn on Stolen Device Protection if your iOS version offers it. Hide Ledger Live previews on the lock screen and in notifications. Keep iOS updated, install apps only from the App Store, and avoid jailbreaking. On the Ledger side, set a PIN, enable a passphrase if you use hidden wallets, and store the recovery phrase offline on metal or paper. Do not save the recovery phrase in Notes, Photos, iCloud, or any app on the phone.
Why won’t my Ledger device pair with Ledger Live on iPhone?
Check the basics first: Bluetooth on, Ledger powered on and you have entered its PIN, device charged, and no other phone or computer connected to it. Open Ledger Live, go to My Ledger, and follow the add-device steps. If it still fails, toggle Bluetooth off and on, remove the old Ledger entry from iOS Bluetooth settings, restart the iPhone and the Ledger, then try again. Check that Ledger Live has Bluetooth permission in iOS Settings. If your Ledger firmware is old, update it with Ledger Live on a computer over USB. Also close other wallet apps that may hold the Bluetooth connection. For Nano X, make sure Bluetooth is enabled on the device itself if your model has that setting.
What happens if I lose my iPhone with Ledger Live installed?
Your crypto does not disappear. Ledger Live is a viewing and transaction app; the private keys stay on your Ledger hardware wallet. If you lose the phone but still have the Ledger and your recovery phrase, install Ledger Live on a new iPhone, connect the Ledger, and add your accounts again. If the phone is lost or stolen, erase it remotely through iCloud, change your Apple ID password, and sign out of other devices. If your Ledger is also lost, restore your wallet from the recovery phrase onto a new Ledger device. Anyone who finds the phone may see balances if they can get past the lock screen, but they cannot move funds without the Ledger device and its PIN. Never share your recovery phrase.
Can I set up Ledger Live on iOS without a Ledger device, and what does the app need from my iPhone during pairing?
Ledger Live for iOS is a companion app. You can install it from Apple’s App Store and browse some features, but you cannot create a hardware-backed crypto account or send funds without a compatible Ledger device. On iOS, Ledger Live uses Bluetooth, so supported models include Ledger Nano X, Ledger Stax, and Ledger Flex. Ledger Nano S and Nano S Plus do not work with Ledger Live on iPhone because they lack Bluetooth and iOS does not support the needed cable connection in the app. To pair: turn on the device, enter your PIN on the device, enable Bluetooth on the device, enable Bluetooth on iPhone, open Ledger Live, choose Add device / My Ledger, select your model, and approve the pairing code on the Ledger screen. Then add accounts and install apps as needed. The app never needs your 24-word recovery phrase. If any app or website asks for it, stop and treat that as a scam. Confirm every address and transaction on the Ledger screen, not just on the iPhone.
My Ledger Nano X keeps disconnecting from Ledger Live on my iPhone. What can I try before resetting the device?
Try simple Bluetooth checks first. Charge the Nano X, enter its PIN, and open its control center by pressing both buttons. Make sure Bluetooth is On. On the iPhone, open Settings > Bluetooth and confirm the Nano X appears. Close other wallet apps and any desktop Ledger Live session that may be holding the connection. Toggle iPhone Bluetooth off and on, then reopen Ledger Live. If the app still does not see the device, go to My Ledger, remove the device entry, and pair it again. You can also reset Bluetooth pairing on the Nano X from its control center, then pair from scratch. Restart both the iPhone and the Nano X. Check that iOS and Ledger Live are updated from the App Store. If the device only fails on iOS but works with USB on a computer, use desktop Ledger Live to update firmware. If nothing works, contact Ledger Support with your device model, iOS version, Ledger Live version, and the exact error message. Never share your recovery phrase with anyone, including support.
Should I use Ledger Live on a jailbroken iPhone, and which iOS security settings matter most for crypto?
A jailbroken iPhone weakens the security model that Ledger Live depends on. The Ledger hardware wallet still keeps private keys inside the device, so a jailbroken phone does not directly expose your seed. But jailbreaking can allow malware to read the screen, capture keystrokes, alter copied addresses, record network traffic, or trick you into signing a transaction you did not intend. For that reason, use a non-jailbroken iPhone with a current iOS version for crypto management. Set a long alphanumeric passcode, enable Face ID or Touch ID, and turn off lock-screen notification previews for Ledger Live. Keep iOS and Ledger Live updated from the App Store. Avoid unknown configuration profiles, mobile device management profiles, and sideloaded apps. Keep Bluetooth off when you are not pairing. Do not screenshot or store your recovery phrase on the phone. Verify every transaction amount, fee, and destination address on the Ledger device screen. If you need extra separation, use a dedicated iPhone for crypto and keep the recovery phrase offline on paper or metal. If you already used Ledger Live on a jailbroken phone, move the recovery phrase to a clean offline storage method, check your accounts for unexpected transactions, and consider generating a new wallet with a new recovery phrase if you suspect the phone was compromised.
From October 6 to 8, the 22nd Annual International Conference “European Athletes as Students” (EAS) will take place at the University of Latvia in Riga, Latvia.
This year’s main theme, “Dual Careers of Elite Athletes: Integrating Sport and Education for Future Success,” focuses on how educational systems and sports organizations can collaborate to ensure a sustainable future for athletes.
The EAS Conference has become an important annual platform for the exchange of knowledge and experience among representatives of sports federations, universities, and sports schools, ERASMUS+ project partners, and dual career experts. The event features presentations of scientific research, examples of best practices, and opportunities for developing cooperation in future projects. Traditionally, the conference also includes the presentation of the Bengt Nibelius Scholarship, awarded to outstanding young researchers in the field of dual careers.
This year’s conference will gather around 70 participants from 16 European countries and Brazil—including professors, researchers, representatives of national Olympic committees, sports schools and academies, as well as students. Among the participants will also be representatives from the European Parliament, the Latvian Ministry of Education and Science, the Latvian Olympic Committee, the Latvian Basketball Association, and international organizations such as FISU and ENGSO.
Conference participants will explore innovative strategies and policy frameworks that support the academic and athletic development of young athletes. The program will also include practical examples from leading European universities (in Spain, Italy, and Germany), youth sports schools (in Denmark and Finland), as well as experiences from Brazil. Discussions and working groups will serve as a platform for developing new ideas and projects in the field of dual careers.
Professor Ilvis Abelkalns of the University of Latvia emphasizes:
“For the University of Latvia, this is an excellent opportunity to demonstrate its commitment to supporting student-athletes’ education, while also learning from practices implemented elsewhere in Europe. It is also a chance to contribute actively to the work of EAS—for example, the ERASMUS project ‘More than Gold’ initiated by the University of Latvia in 2021 developed guidelines for governments and universities that formed the basis for including dual career provisions in the new edition of the Latvian Sports Law.”
The open and friendly atmosphere of EAS conferences has always encouraged the creation of new initiatives, strengthened cooperation, and fostered the development of lasting professional relationships.
The official conference page: https://eas2025.lu.lv/

The EU Funding & Tenders Portal is a crucial tool to find new opportunities and information on EU-funded projects. The recent implementation of the Portal allows a friendly use search through enhanced filtering, provides new recommendations tailored to specific needs, and informs through the News and Events sections.
In particular, information on 2021-2027 EU-funded dal career projects is available at https://ec.europa.eu/info/funding-tenders/opportunities/portal/screen/opportunities/projects-results?keywords=Dual%20Career&programmePeriod=2021-2027&order=DESC&pageNumber=1&pageSize=25&sortBy=title
Further information on the new portal and videos are available at https://ec.europa.eu/info/funding-tenders/opportunities/portal/screen/home
Vavada kazino spēļu mājas lapa Latvijā 2026 gadā
Pirmais solis, kas jāveic, ja vēlaties izbaudīt azartspēļu piedzīvojumu no savām mājām, ir apmeklēt vavada lv. Šī platforma piedāvā plašu spēļu klāstu, kas piesaista gan iesācējus, gan pieredzējušus spēlētājus. Izvēlots no augstākas kvalitātes ražotājiem, spēļu automāti un galda spēles nošķir šo vietni no citām.
Papildus izcilai spēļu izvēlei, šī vietne sniedz lietotājiem iespēju piedalīties dažādās akcijās un bonusa piedāvājumos, kas ļauj palielināt uzvaru iespējas. Ja meklējat optimālu pieredzi, noteikti pievēršiet uzmanību arī sistēmai, kas nodrošina ātru un drošu maksājumu veikšanu, kā arī ērti lietojamu saskarni.
Vērts pieminēt, ka spēļu pieredze tiek pastāvīgi uzlabota, piedāvājot jaunākās funkcijas un spēles, tādēļ ikviens var atrast kaut ko jaunu un aizraujošu. Nezaudējiet laiku un izpētiet platformu, kas ir izvirzījusies kā viena no labākajām iespējām azartspēļu entuziastiem.
Spēļu piedāvājuma daudzveidība un populārākās spēles
Izmēģiniet dažādas spēles, lai atrastu savas iecienītākās. Lielā platībā ir vairāki spēļu veidi, sākot no tradicionālajiem ruletes un pokera variantiem līdz modernām laika nišām. Džekpoti un bonusi spēlēm piešķir papildu pievilcību, tāpēc īpaši populāri ir tieši spēļu automāti ar progresīvajiem džekpotiem, kas vairākkārtīgi pārsniedz sākotnējā ieguldījuma summu.
Populāras spēles un to raksturojums
Daži no spēļu variantiem, kas izceļas lielā spēlētāju interesi, ir:
| Spēle | Tips | Iespējamie laimesti |
|---|---|---|
| Starburst | Laika niša | Līdz 50 000x likmei |
| Roulette | Galda spēle | 2,7% mājas mala |
| Teksas Hold’em | Karti | Atkarīgs no vērpienu |
Papildus augstākminētajām spēlēm ir arī citas, kas piesaista uzmanību ar īpašajiem bonusiem un bezmaksas griezieniem. Neaizmirstiet izpētīt jaunas izlaišanas, jo katru mēnesi parādās aizraujošas inovatīvas spēles, kas var piedāvāt unikālas funkcijas un pievilcīgas spēles pieredzi. Regulāri piedāvājumi un akcijas nodrošina vēl lielāku iespēju gūt panākumus. Klients var viegli apmierināt savas prasības un atrast ideālo spēli savam stilam.
Bonusu un akciju iespējas Latvijas spēlētājiem
Ja Tevi interesē kā piesaistīt papildu līdzekļus savam spēļu kontam, pievērs uzmanību sagaidīšanas bonusiem, kas pieejami jaunajiem spēlētājiem. Lielākā daļa platformu piedāvā dāsnu pirmo iemaksu bonusu, kas parasti ir procentuāla daļa no veiktā iemaksas apjoma. Piemēram, Tu vari saņemt 100% bonusu līdz noteiktai summai, tas nozīmē iespēju saņemt dubultu naudu savam spēļu kontam.
Reģistrācijas kārtība
Reģistrējoties, ir svarīgi pārliecināties, ka esi izvēlējies visizdevīgāko piedāvājumu. Izpēti, vai bonusam ir pievienoti izspēles termiņi un pārliecinies, ka tie Tev ir izpildāmi. Katrs bonuss nāk ar saviem nosacījumiem, tādēļ svarīgi tos izlasīt, pirms piekrīti. Tev palīdzēt var arī atsauksmes no citiem spēlētājiem, kas jau ir izmantojuši konkrēto akciju.
Regulārie spēlētāji var gūt labumu no dažādām akcijām, kas tiek rīkotas iknedēļas vai ikmēneša ietvaros. Parasti šīs akcijas ietver bezmaksas griezienus vai bonusus bez iemaksas, kas dod iespēju spēlēt bez papildu riska. Lai nepalaistu garām šādus piedāvājumus, novērtē platformas komunikācijas kanālus – e-pastus un sociālos tīklus.
VIP programmas
Ja esi aktīvs spēlētājs, pievērs uzmanību VIP programmām, kas bieži tiek piedāvātas. Šīs programmas palīdz Tev iegūt individuālas priekšrocības, piemēram, augstākus bonusus un īpašus piedāvājumus. Jo vairāk spēlē, jo labākas privilēģijas vari saņemt – no ekskluzīvām balvām līdz pat ceļojumiem un pasākumiem.
- Uzkrāj punktus, spēlējot un izmanto tos vēlāk.
- Saņem individuālu menedžeri, kas palīdzēs sarunāt labākos piedāvājumus.
- Piedalies īpašajās turnīros ar lielām balvām.
Neaizmirsti arī par lojalitātes programmām! Lielākā daļa platformu atbalsta tādas, kur varēsi saņemt punktus par katru veiktu likmi, kas pēc tam tiks apmainīti pret īstām naudām, griezieniem vai citām balvām.
Beigās noteikti pārbaudi piedāvātos draugu aicināšanas bonusus. Šīs akcijas ļauj Tev saņemt papildu naudu vai griezienus, ja aicini savus draugus pievienoties platformai. Tas ir izdevīgi abām pusēm – Tu saņem bonusus, un arī Tavs draugs gūst labumu no sākotnējiem piedāvājumiem.
Drošība un lietotāju atbalsts Vavada platformā
Regulāras drošības pārbaudes ir neatņemama platformas darbības daļa. Katram lietotājam ieteicams veikt divu faktoru autentifikāciju, kas nodrošina papildu aizsardzību pret neautorizētu piekļuvi. Šāda pieeja samazina riskus, kad runa ir par personīgo datu un finanšu informācijas aizsardzību. Visiem darījumiem tiek izmantota šifrēšana, tādējādi garantējot, ka sensitīvie dati paliek slepeni un droši.
Klientu atbalsta pakalpojums ir pieejams 24/7, un tas sniedz iespēju nekavējoties atrisināt jebkuru radušos problēmu. Veicot saziņu ar komandu, lietotāji var izmantot čatu, e-pastu vai telefonu. Atbildes tiek sniegtas ātri un skaidri, kas ievērojami uzlabo lietotāju pieredzi. Ja rodas jautājumi par konta verifikāciju vai spēļu noteikumiem, ekspertu komanda ir gatava sniegt nepieciešamo atbalstu.
Ikviens lietotājs aicināts iepazīties ar platformas drošības politiku, kas ietver detalizētu informāciju par datu apstrādi un aizsardzību. Viens no svarīgākajiem elementiem ir atbildīga spēle, kas ietver pašnovērtējuma rīkus un iespēju ierobežot spēlēšanas laiku. Uzmanība pret šo aspektu veicina ne tikai individuālo drošību, bet arī vispārēju labklājību gan spēlētāju, gan platformas līmenī.
Activate Windows 11 and Office with KMS Auto Win 11: Step-by-Step Activation Tool Guide
KMS Auto Win 11 is a popular activation tool designed to help users activate Windows 11 and Microsoft Office products easily. This tool works by using the Key Management Service (KMS) method, which allows for automatic activation without the need to enter a product key manually. Many people look for ways to activate their Windows 11 operating system and Office suite to unlock all features and enjoy a fully functional experience. KMS Auto Win 11 provides a simple and effective solution for this purpose.
Using KMS Auto Win 11, users can activate their Windows 11 system quickly, ensuring that the operating system is genuine and fully supported by Microsoft. The activation process is straightforward and requires only a few steps, making it accessible even for those who are not very tech-savvy. This tool also supports activating different versions of Microsoft Office, allowing users to benefit from all the features of their Office applications without restrictions.
One of the main advantages of KMS Auto Win 11 is that it automates the activation process, reducing the risk of errors that can occur when entering product keys manually. It also helps users avoid the need to purchase expensive licenses by providing a free activation method. However, it is important to use such tools responsibly and understand the legal implications of software activation.
How to Use KMS Auto Win 11 for Windows 11 Activation and Office Products
KMS Auto Win 11 is a helpful tool that makes activating Windows 11 and Office products easy. This tool uses the kms activator for windows to automatically activate your software without needing to enter a product key. The windows 11 activation method it uses is simple and fast, making it a popular choice for many users.
The kms auto activation process runs quietly in the background, so you don’t have to worry about complicated steps. This windows 11 activation utility ensures your system is genuine and fully functional. Following a windows 11 activation guide can help you understand how to use this tool safely and correctly.
Using the kms auto activator, you can activate both Windows 11 and Microsoft Office products with just a few clicks. This saves time and avoids errors that happen when typing keys manually.
System Requirements for KMS Auto Win 11 Activation Tool
Before using the kms auto win 11 tool, make sure your computer meets these requirements:
| Requirement | Details |
|---|---|
| Operating System | Windows 11 (all editions) |
| RAM | Minimum 2 GB |
| Disk Space | At least 100 MB free |
| Administrator Rights | Required for installation |
| Internet Connection | Recommended for activation |
Having these requirements ensures the kms auto activation process works smoothly and without interruptions.
Step-by-Step Guide to Download and Install KMS Auto Win 11
- Download the kms auto win 11 tool from a trusted source.
- Disable antivirus temporarily to avoid interference.
- Extract the downloaded file to a folder on your PC.
- Right-click the setup file and select “Run as administrator.”
- Follow the on-screen instructions to complete installation.
- After installation, open the windows 11 activation utility.
This simple process helps you get started with the kms activator for windows quickly and safely.
Setting Up KMS Server and Using Windows 11 Activation CMD
To activate Windows 11 using the kms auto activator, you need to set up the KMS server:
- Open Command Prompt as administrator.
- Enter the command to set the KMS server address.
- Use the windows 11 activation CMD commands to connect to the server.
- Run the activation command to start the kms auto activation process.
This method is part of the windows 11 activation guide and ensures your system connects properly to the KMS server for activation.
How to Activate Windows 11 and Office Using KMS Auto Win 11
Activating Windows 11 and Office products with kms auto win 11 is easy:
- Launch the kms auto win 11 tool.
- Choose the product you want to activate (Windows 11 or Office).
- Click the “Activate” button to start the kms auto activation process.
- Wait a few moments for the tool to complete activation.
- Restart your computer to apply changes.
This windows 11 activation method guarantees your software is genuine and fully functional.
Common Windows 11 KMS Keys and Activation Methods
Here are some common KMS keys used with the kms auto activator:
| Product | KMS Key Example |
|---|---|
| Windows 11 Pro | W269N-WFGWX-YVC9B-4J6C9-T83GX |
| Windows 11 Enterprise | NPPR9-FWDCX-D2C8J-H872K-2YT43 |
| Office 2019 Pro Plus | NMMKJ-6RK4F-KMJVX-8D9MJ-6MWKP |
These keys work with the kms auto activation process to activate your software without hassle. Using the right windows 11 activation method helps keep your system secure and fully operational.
Key Features, Benefits, and Solutions of KMS Auto Win 11 Activation Software
KMS Auto Win 11 is a powerful windows 11 activation software that helps users activate their Windows 11 and Office products quickly and easily. This kms auto activation tool offers a reliable windows 11 activation solution by automating the process, so users don’t need to enter product keys manually. It works as a kms auto activator that connects to a KMS server to provide genuine digital licenses.
This windows 11 activation utility is designed to be user-friendly and efficient, making it a popular choice for those who want to unlock all features of their software without hassle. It supports multiple versions of Windows 11 and Office, providing a versatile activation method.
Features of KMS Auto Win 11 for Windows 11 and Office Activation
- Automatic Activation: The kms auto activation tool automatically activates Windows 11 and Office without manual input.
- Multi-Product Support: Works with various editions of Windows 11 and Microsoft Office.
- No Product Key Needed: Uses KMS technology to activate software without requiring a product key.
- User-Friendly Interface: Simple design that anyone can use without technical knowledge.
- Offline Activation: Can activate Windows 11 even without an internet connection in some cases.
- Regular Updates: Keeps up with the latest Windows and Office versions for compatibility.
- Safe and Secure: Minimizes risks of errors during activation.
“KMS Auto Win 11 provides a seamless activation experience for users needing a quick and effective windows 11 activation solution.”
Advantages of Using KMS Auto Win 11 Activation Tool
- Cost-Effective: Avoids the need to purchase expensive licenses.
- Time-Saving: Activates software in just a few clicks.
- Error Reduction: Automates the process, reducing manual mistakes.
- Wide Compatibility: Supports multiple Windows 11 editions and Office versions.
- No Technical Skills Required: Easy for beginners to use.
- Portable Utility: Can be run from a USB drive without installation.
- Reactivation Capability: Allows reactivation if Windows or Office updates reset activation status.
How KMS Auto Win 11 Provides Digital License Activation Without Product Key
The kms auto activator works by emulating a Key Management Service server on your PC. Instead of entering a product key, the windows 11 activation utility sends a request to this virtual server, which then issues a digital license to activate Windows 11 or Office.
| Step | Description |
|---|---|
| 1. Setup KMS Server | The tool sets up a local KMS server environment. |
| 2. Activation Request | Windows or Office sends activation request. |
| 3. License Issued | The KMS server responds with a digital license. |
| 4. Activation Complete | Software is activated without a product key. |
This process ensures genuine activation without the need for purchasing or entering a product key manually.
Troubleshooting Windows 11 Activation Process with KMS Auto Win 11
If activation fails or errors occur, try these steps:
- Run as Administrator: Ensure the kms auto activation tool is run with admin rights.
- Disable Antivirus: Temporarily turn off antivirus software that may block activation.
- Check Internet Connection: Some activation methods require online access.
- Reboot System: Restart your computer after activation attempts.
- Update Tool: Use the latest version of the windows 11 activation utility.
- Clear Previous Keys: Remove old product keys using Command Prompt before activating.
- Verify Windows Version: Confirm your Windows 11 edition is supported by the kms auto activator.
“Following these troubleshooting tips can help resolve common issues during the windows 11 activation process.”
KMS Auto Win 11 Activation Utility vs Other Windows 11 Activation Software
| Feature | KMS Auto Win 11 Activation Utility | Other Activation Software |
|---|---|---|
| Ease of Use | Very simple interface | Often complex or confusing |
| Activation Method | KMS-based digital license | Various, including key generators |
| Product Support | Windows 11 and Office | May support fewer products |
| Safety | Minimizes risk of errors | Some tools may cause system issues |
| Cost | Free | Some require payment |
| Updates | Regular updates for compatibility | Updates may be infrequent |
| Offline Activation | Supported | Often requires internet |
KMS Auto Win 11 stands out as a reliable and user-friendly windows 11 activation solution that balances safety, ease, and effectiveness better than many alternatives.
Frequently Asked Questions About KMS Auto Win 11 Activation Tool
Many users have questions about the kms auto activation tool and how it works with Windows 11. This section answers common queries related to the windows 11 activation process using the kms auto activator and windows 11 activation software.
The kms auto activation tool is designed to simplify the windows 11 activation process by automating it. It helps users avoid manual entry of product keys and provides a digital license through a virtual KMS server. Understanding how this tool works and its limitations can help users activate their systems smoothly.
Can I Activate Windows 11 Without a Product Key Using KMS Auto Win 11?
Yes, the kms auto activator allows you to activate Windows 11 without entering a product key manually. This is possible because the windows 11 activation software uses a virtual KMS server to issue a digital license during the activation process.
- The kms auto activation tool sets up a local KMS server on your PC.
- Windows 11 sends an activation request to this server.
- The server responds with a digital license, completing activation.
This method is part of the windows 11 activation guide that many users follow to activate their system easily and quickly.
Is KMS Auto Win 11 Safe to Use for Windows 11 Activation?
The kms auto activation tool is generally safe when used correctly. It automates the windows 11 activation process, reducing errors that can happen with manual key entry. However, users should be cautious and ensure they download the windows 11 activation software from trusted sources.
- Always disable antivirus temporarily during activation to avoid interference.
- Run the kms auto activator as an administrator.
- Follow the windows 11 activation guide carefully to avoid mistakes.
Using the tool responsibly helps maintain system stability and security during activation.
How Long Does the Windows 11 Activation Last with KMS Auto?
The activation provided by the kms auto activator usually lasts for 180 days. After this period, the windows 11 activation process needs to be repeated to renew the digital license.
| Activation Duration | Renewal Requirement |
|---|---|
| 180 days | Reactivate using kms auto tool |
The kms auto activation tool can be used multiple times to keep Windows 11 activated without needing a new product key.
Can KMS Auto Win 11 Activate Both 32-bit and 64-bit Windows 11 Versions?
Yes, the kms auto activation tool supports activating both 32-bit and 64-bit versions of Windows 11. This makes it a versatile windows 11 activation software suitable for different system architectures.
- Compatible with all Windows 11 editions.
- Works on both 32-bit and 64-bit systems.
- Supports activation of Microsoft Office products as well.
This flexibility is part of why many users prefer the kms auto activator for their activation needs.
What to Do If Windows 11 Activation Fails Using KMS Auto Win 11?
If the windows 11 activation process fails with the kms auto activation tool, try these troubleshooting steps:
- Run the kms auto activator as an administrator.
- Temporarily disable antivirus or firewall software.
- Check your internet connection if online activation is required.
- Restart your computer and try the activation again.
- Use the latest version of the windows 11 activation software.
- Clear any previous product keys using Command Prompt before retrying.
“Following these steps can help resolve most issues during the windows 11 activation process with the kms auto activation tool.”
Dear Dual Career Friends and Colleagues,
Christmas is a time for love, reflection on recent activities, inspiration and hope to renew our good will toward dual career. The sportspersons need dual career to contribute greatly to the society and our singular mission is to improve their opportunities to combine and progress their sports, education, and working life.
In the past months EAS continued the discussion of specific dual career issues through virtual cafes dedicated to the educational and employment perspectives, dual career as a means of European sports diplomacy, and the alignment of sports and working values. Furthermore, a large participation to the 20th EAS Conference in Gaeta, Italy, substantiated the growing interest in uncovering dual career aspects and stimulating a fruitful dialogue for the promotion of wellbeing of the sportspersons. Surely, proposals from our members for addressing new topics will be greatly appreciated.
In agreement with the aims of the Network, in 2023 EAS contributed to the finalization of three very successful ERASMUS+Sport Collaborative Partnerships dedicated to empower dual career athletes with entrepreneurship skills (ELCAMP), para-sports (Para-Limits), and the employee-sportspersons (BRAVA-DC), to the first phases of a Collaborative Partnerships dedicated to (Talent), and a Capacity Building (Sports as Value), and in the 2004 it will be involved in new ones (DC Mentor, DiscoverU, FIND ME, and Smart Start for DC). Furthermore, EAS also contributed to the publications of the book “A holistic approach to the dual career of the student-athlete”, a paper on the self-perception of dual career developed during the Para-Limits project published on a peer-review journal.
During this year, EAS consolidated fruitful partnerships with International Organizations in Sports through the participation in relevant events organized at European (e.g, Erasmus+ Infoday, 2023 European Sport Forum, Bureau of the “Consultative Committee of EPAS – Council of Europe”, Dual Career Day at the University of Naples, Italy)) and international (2023 Sport Forum, Soochow University, China) levels. Finally, a Memorandum of Understanding between EAS and the Italian Scientific Society of Movement and Sports (SISMES) was signed, and the President of EAS received a Medal of Appreciation from EUSA for her dedication to dual career.
During the Annual General Assembly held in Gaeta, Italy, the analysis of the responses to the EAS survey relative to the past and future actions of EAS was discussed to direct the Strategic Plan for the 2023-2026 quadrennium to be presented during the 2024 EAS Conference to be held in Katowice, Poland.
As we enter the New Year, we shall reaffirm our determination to support dual career sportspersons with great enthusiasm and passion. We are grateful to work with such a dedicated community and we are looking forward to remaining inspired by renewing the 2024 EAS membership through the link http://www.dualcareer.eu/membership/.
We extend our very best wishes for a Merry Christmas and a bright New Year to you and your beloved ones.
The EAS Board
REG. NUMBER: Voluntary Organisation registration VO/1270
PIC NUMBER: 913459865
Email: info@dualcareer.eu