Author: duponam

The 21st EAS Virtual Cafè on “Dual career in Sport, the Spirit of Humanity: Protecting the Sport Person” will be organized online next May 18 (Monday), 2026 at 13:00 (CET).
This event is organized in conjunction with the European projects FOCUS (ERASMUS-SPORT-2025-SCP-101243801) and “Give Sport a Say” (CERV-101253838). Whilst FOCUS aims to establish an innovative and scalable Dual Career co-created framework, ensuring that elite football players can successfully transition from youth to professional sport levels while maintaining educational and career opportunities, Give Sport a Say aims to foster the civil dialogue on future of sport policy in connection with health, equality and youth, Therefore, your participation for the advancement of the European sport dialogue will be highly appreciated.


Programme:
13:00 Welcome – Moderator
Mrs. Olga Papale, PhD Europaeus
Mrs. Olga Papale, kinesiologist. In 2025 she has been awarded the Bengt Nybelius Scholarship and the Special Mention as Youth Researcher by the Italian Society of Sport and Movement Sciences (SISMES). Her research focuses on physical activity, health promotion, outdoor exercise, and student-athlete wellbeing, with particular attention to dual career pathways and sustainable sport participation.
13:05 ”Building the FOCUS project on identified needs and evidence”
Mr. Aki-Matti Alanen, PhD
Mr. Aki-Matti Alanen, kinesiologist. He is the Sports Development Manager at the Kolmen Kampuksen Urheiluopisto OY – Sport Institute of Three Campuses (KKU), Finland, with responsibility for research, development, innovations, coach education, planning and utilization. In working closely with elite youth athletes through coaching support, well-being, testing and training, and career progression, within the FOCUS project Mr. Aki-Matti Alanen has analysed the current state of dual career in European Nordic countries,
13:15 ”Give Sport a Voice, Give Athletes a Future: Dual Career & Human Dignity in Sport”
Mrs. Sara Massini
Mrs. Sara Massini, psychologist, is the head of European and International affair department of OPES, Italian umbrella organization for grassroots sport under the Italian Olympic Committee structure. Former secretary general of ENGSO and youth leader within the Italian youth Council and European youth forum, she has a long experience in advocacy, policy and project management in the areas of sport and youth both at National and European levels. For OPES, Mrs. Sara Massini is the leader of the Give Sport a Say project.
13:25 “Dual career across a Portuguese football club”
Mr. Francisco Graça
Mr. Francisco Graça is a UEFA C Football Coach, assistant coach and physical trained of youth soccer players at the professional football club Associação Académica de Coimbra, Portugal, he is enrolled at the MSc in Sports Training of the University of Coimbra.
13:35 “Beyond the Ice Track: Sport and Dual Career United”
Mr. Ivo Steinbergs
Mr. Ivo Steinbergs, former international skeleton athlete, graduated at the Riga Technical University. With a strong experience in building national programs and preparing athletes for international competitions, he joined Bobsleigh Canada Skeleton as an official coach for the skeleton team during the 2022 Beijing Olympic Winter Games and he is the coach of the Skeleton Latvian Team qualified for the 2026 Olympic Winter Games. S Mr. Ivo Steinbergs has a strong background in programming performance development, track preparation, and athlete development systems.
13:45 “Nothing Is Guaranteed in Sports: Why Athletes Need a Dual Career”
Mr. Janis Leitis
Olympic track and field athlete and Latvian national record holder in the 400-meter sprint, Mr. Janis Leitis is a nutrition specialist with a professional experience in relation to physical health, physical exercise, and recovery processes. He is a Lecturer at the Riga Stradiņš University, Latvia.
13:55 General discussions and invitation to the EAS Annual Conference and elections to be held in Oulu, Finland on October 5-7, 2026.
You can join the Zoom Meeting at https://uni-lj-si.zoom.us/j/97371548061 (Meeting ID: 97371548061).
Ledger Live Mac Not Opening: Step by Step Through Launch Faults After Upgrades or Migrations
Troubleshoot Ledger Live Mac Not Opening by isolating which of three layers fails: the download, the application bundle, or the network path. A bouncing icon that never resolves, a window that disappears in under a second, and a window that appears but stays blank point to different layers. Work from the outside in, and keep the hardware device disconnected until you know which layer you are dealing with.
What the Launch Sequence Does on an Apple Desktop
Launching the companion application on an Apple desktop runs a fixed sequence: the system checks the bundle’s code signature and quarantine flag, loads the executable for the computer’s processor, draws the interface, then establishes outbound connections to read account data. A break at any link produces a different symptom, so the symptom itself narrows the cause.
Code Signature and Quarantine Flags Come First
The first gate is the code signature, and a bundle that fails it is refused before any window is drawn. The Apple operating system records where each download came from in a quarantine attribute and declines to run software whose signature differs from the identity the developer registered. A file fetched through a browser carries that attribute automatically; a file copied from a local archive or a shared drive may carry one inherited from the archive, or none at all. Either state can stop the launch with no dialog on screen.
Processor Translation on Apple Silicon Hardware
The second gate is processor compatibility, and it decides whether the executable can begin at all. A build compiled only for Intel chips has to pass through the translation layer Apple ships, and that layer expects an intact, correctly signed bundle; edit the bundle after signing and the translation refuses it. The two hardware generations therefore fail differently: on Apple silicon the process vanishes within a second, while on older Intel desktops the icon bounces and the window stays empty.
What a Blank Window Says About the Network Path
A window that appears and then stays blank usually means the interface loaded and the first outbound request never completed. The client has to reach remote services before it can display balances, so a blocked socket, a captive portal, or a virtual private network that reroutes traffic leaves the window on screen with no content inside it. This separates a connectivity fault from a binary fault: the signature passed, the executable ran, and the break sits after the interface is drawn.
Owners Who Meet This Fault, and the Situations That Trigger It
The people affected are self-custody owners who manage accounts, install device firmware, and move assets from a desktop rather than a phone. The trigger is almost always an environmental change: a point upgrade of the Apple operating system, a migration to new hardware, a fresh user account, or a reinstalled bundle. New installs on untouched systems rarely fail this way.
Long-Running Installations After a System Upgrade
An installation that has survived two or three system upgrades is the most frequent case, because the bundle keeps its old permissions while everything around it changes. Each annual release tightens which processes may read protected folders, which may hold network sockets, and which signed components the loader accepts. The bundle itself is untouched, so no file looks altered in a directory listing, yet the launch is refused. Replacing it with the current release settles more of these cases than any other single action.
Desktops Migrated to New Hardware
The migration tool copies the bundle together with its preferences and cached data, and those files carry identifiers written on the previous computer. A cache describing different hardware can make the client quit while it reads its own state, before the interface is drawn. Letting a current release rebuild that cache from the hardware device is cleaner than repairing the transferred copy. This path applies to anyone who moved from an Intel desktop to an Apple silicon model, and less often to a same-generation replacement.
Shared Desktops and Restricted Accounts
On a family or managed desktop, the account running the client may lack write access to the folders it uses for cached data. The same restriction appears on accounts governed by a management profile, which can block executables that lack administrator approval. Running one launch from an administrator account tells you whether permissions are the cause. If the client starts there and quits in the limited account, the remedy belongs in the account settings rather than in the application itself.
Four Routes to a Working Copy, Compared
Four routes put a usable copy on the computer: a fresh installer from the publisher, the bundle already present before an upgrade, a copy restored from a local backup, and a build obtained elsewhere. They differ in how much stale state they carry and how far the source can be traced, which decides the time each route saves or spends.
The comparison weighs four acquisition routes against three criteria that matter after a launch has already failed once: whether the route suits your situation, what it leaves behind on disk, and how far the source can be traced. Version numbers, file sizes and system requirements shift between releases, so the manufacturer’s published page stays authoritative.
| Route | Fits when | Main limit | How to confirm the source |
|---|---|---|---|
| Installer downloaded from the publisher’s own site | First install, or after the client stopped starting | Needs a stable connection and free disk space | Publisher name and version match the official release page |
| Bundle already on disk before a system upgrade | The client ran well on the previous system release | Carries permissions and caches written by the older system | Version listed in the application’s own information panel |
| Copy restored from a local backup snapshot | A recent snapshot exists from the same system generation | Brings back stale caches and preferences alongside the app | Snapshot date compared with the date of the current release |
| Build from a mirror, forum attachment, or sponsored search result | No legitimate case; the source lacks a traceable link to the publisher | Carries unknown code, often inside a fake installer wrapper | Signature and publisher shown in the system’s file information panel |
A fresh installer suits any situation where the manufacturer’s own page is reachable and there is room for a second copy; it suits a metered or administratively locked connection poorly. The bundle already on disk suits the case where the previous system release worked and the upgrade is the only change, and stops suiting once that bundle has been edited or repaired by hand. A snapshot restore suits a computer whose system generation is unchanged; across generations, restored preferences describe an environment the hardware no longer has. Unofficial builds suit no scenario at all.
What a Publisher Signature Establishes
A signature establishes who built the file and whether it has been altered since, and it establishes no more than that. It confirms the developer identity the operating system expects, and it detects any edit made after signing, which is why a repaired or hand-modified bundle stops launching. It gives no indication of whether the version is current, whether it suits the computer’s processor, or whether the download page itself was the genuine one. Those questions are answered by the published release page and by the system’s own information panel.
What a Snapshot Restore Brings Back Besides the App
A snapshot restore returns the executable, its preferences, its caches, and any helper components that were registered at the time. That is useful when one file was corrupted and the rest of the environment is unchanged, and it becomes a liability when the system generation has moved on, because restored preferences can point at folders or services that no longer exist in the same form. Restoring only the application folder, rather than the whole user directory, keeps most of that stale state out of the way.
Which Repairs Are Irreversible, and Which Mistakes Cause Them?
Deleting the application folder, clearing its caches, and reinstalling from the publisher’s page are reversible, and none of them touches funds, which reside on the hardware device and in the recovery phrase. The irreversible mistakes are typing that phrase into a dialog, approving a signature warning, and forcing a downgrade after a newer release has written to the data folders.
Keys Reside on the Device, Away From Application Data
The accounts and keys are held by the hardware device, and the desktop software acts as a viewer and a coordinator rather than a store. That design is why clearing caches, removing the bundle, and starting over carry no risk to balances: no file in the user folder is required to spend, sign, or recover. The consequence matters more than the rule, because any dialog asking for the recovery phrase during a launch repair is either a misunderstanding of that design or an attempt to capture it.
Signature Warnings Are a Stop Signal
When the operating system reports that a developer’s identity is unverified, it is describing a mismatch between the signature on the file and the identity the system can check. Bypassing that warning through a system setting removes the only automatic check standing between an altered download and your computer. The right response is to delete the file, return to the manufacturer’s own page, and compare the version and publisher shown in the system’s file information panel. A file that fails that comparison should never be run.
Downgrades Can Write Beyond Repair
Moving back to an earlier release is risky because a newer build may already have migrated the local data folders into a format the older code is unable to read. Once that migration happens, the older build may fail to recognise its own files, and the state is recoverable only from the hardware device, which is harmless for funds and inconvenient for settings. Before attempting a downgrade, copy the application’s data folder aside, and check whether the older release is still published on the manufacturer’s support pages.
How Do You Confirm Whether the App or the System Is at Fault?
You confirm it by testing the same build under conditions the failing setup lacks: a second user account, a different network path, and the system’s own signature report. Have ready the exact version string, the system release number, and the name of the file you installed. Five checks separate a broken download from a blocked system.
Step 1: Capture the version and the system release
Record the version string and the system release number before changing anything. Both values decide which of the later comparisons are meaningful, and a failing launch may leave no way to read them from inside the interface.
Step 2: Repeat the launch in a clean account
Run one launch from a second, freshly created user account. A new account carries no inherited preferences, no cached state and no management restrictions, so a successful start there points at the original account’s stored settings rather than at the executable.
Step 3: Read the publisher line
Inspect the file’s publisher and signature in the system’s information panel. Select the application in the folder view, choose the information option, and read the publisher line together with the signature status; a publisher that differs from the manufacturer, or a status marked unverified, means the file was altered or came from another source.
Step 4: Test the network path
Confirm that outbound access is permitted for the application. Check the firewall list, any content filter, and any active virtual private network, then repeat the launch with each one disabled in turn; a window that fills as soon as a tunnel closes identifies the network path as the fault, which no reinstallation will repair.
Step 5: Compare against the published release
Compare your installed version against the one published on the manufacturer’s support pages. If the published release is newer, install that build over the existing one and leave the data folder in place; if the versions match and the launch still fails, the fault sits in the system environment rather than in the download.
Version Drift and the Symptoms Owners Misread
Support windows, minimum system requirements and processor targets move with every release, and the current values are published on the manufacturer’s support pages rather than fixed in any guide. The recurring misreading is treating a blocked window as a corrupted wallet, and treating an instant exit as proof that funds were lost.
Minimum System Requirements Move With Each Release
Each release names a floor for the Apple system version it runs on, and that floor rises as the frameworks the client depends on are retired. A computer left on an older system release installs the application without complaint and then fails to start it, because the check happens at launch rather than at installation. The floor for the current build is stated on the manufacturer’s support pages and changes between releases, so it should be read rather than assumed.
Instant Exits Get Reported as Data Loss
An executable that vanishes immediately is usually failing a signature, architecture, or permission check, and it has read no data and written none. Owners describe that exit as a loss because the interface never appeared and the accounts look absent, when in fact those accounts were never loaded. Connecting the hardware device to a working installation, or reading the same accounts through another compatible interface, separates an empty view from an empty wallet.
Community Advice Ages Faster Than the Binary
Walkthroughs that name particular folders, settings switches, or terminal commands belong to the system generation that existed when they were written, and Apple moves those locations between releases. A command that cleared a quarantine flag on one generation may do no such thing on the next, or may target a path that has since been removed. Where a step references a file path or a menu label, check it against the current system documentation, and treat the manufacturer’s support pages as the reference for anything version-specific.
Here is a standalone HTML article that checks macOS version compatibility before launching Ledger Live, covering system requirements, common failure causes, and a step-by-step verification procedure.
Troubleshoot Ledger Live Mac Not Opening starts with the system release, because the desktop companion exits before drawing a window whenever the installed build sits below the floor the vendor signs for. Two minutes in the About panel and one look at the official download page settle the question. Profiles, downloads and security tools only matter once the release matches.
Check macOS Version Compatibility Before Launching Ledger Live
Compare the installed desktop release against the minimum build the vendor signs for, since the companion application refuses to start when that build sits below the supported floor. Read the version from the About panel under System Settings, General, then match it against the requirement published on the official download page.
How the launcher reads the system build string
Every bundled framework carries a minimum system version stamped into the executable at build time, so the launcher asks the kernel which release is running before it draws a window. When the reply sorts below that stamp, the process exits during dynamic linking and leaves an empty screen behind. The check happens earlier than any window, which makes a version refusal look like a crash or a corrupt file.
Signing and notarization as an independent gate
Signing and notarization form a gate that is independent of the release number, and clearing one has no effect on the other. A download interrupted halfway keeps its quarantine flag, and the system then shows a warning dialog naming an unidentified developer instead of exiting quietly. That dialog is a useful signal: it proves the release check passed and moves the diagnosis toward the file rather than the operating system.
Where the minimum release is published
Supported releases, the exact minimum build and the processor families in scope appear on the vendor’s official download page and in the changelog published with each version. Those numbers move with every major build, and third-party tutorials, mirror downloads and cached forum pages trail behind them by months. Treat any figure from a source other than that page as unverified.
Which Setups Land on the Version Gate, and When It Applies
Three groups run into it: computers held on an older named release, virtual or remote sessions built from a trimmed system image, and restored setups whose backup predates a system upgrade. The gate applies at every launch, so a computer that started the application a year ago can refuse today after an update or a hardware migration.
Computers capped by their newest available release
Apple ends system updates for a processor generation years before the hardware itself gives out, so an older laptop may top out at Catalina or Big Sur while the application’s floor has already climbed past those names. The mismatch is permanent: no setting, reinstall or permission change closes it. A newer computer, or a supported virtual session, is the only route.
Virtual sessions and trimmed system images
Virtualization tools present their own system release to applications, and a virtual disk cloned two years ago keeps reporting that older release however current the host becomes. The same happens inside remote desktop sessions mounted from a server image built for compatibility. A guest system reporting Catalina while the host runs Ventura is the classic case, because the launcher reads the guest and only the guest.
Setups restored from a backup made before an upgrade
A backup taken before a system upgrade restores the older release along with user files when the whole disk is recovered. The application then sees a system build that predates the upgrade its owner believes is installed. Comparing the About panel against the upgrade history settles the question in seconds, and it costs nothing to check before another restore.
How Does a Version Mismatch Compare With Other Launch Failures?
A version mismatch ends the launch with no window and no dialog, and only a system upgrade or a different computer clears it. An incomplete download, a blocked helper service and a damaged profile directory all leave the application visibly present and produce an error the user can read. Separating the four takes minutes and prevents a pointless reinstall.
The table sets a release shortfall beside three other reasons a launch goes nowhere, judged on the visible symptom, the time needed to confirm the cause, and the place where confirmation happens. Every row describes a condition that survives a reinstall, which is why identifying the row first saves an hour of repeated setup.
| Cause | Visible symptom | Time to confirm | Where to confirm |
|---|---|---|---|
| Installed release below the supported floor | No window appears at all | Under a minute | About panel under System Settings, General |
| Partial or quarantined download | System warning naming an unidentified developer | Two minutes | Download folder and bundle signature |
| Security tool blocking the helper service | Window appears, then stalls at connecting | Five minutes | Block log of the security tool |
| Damaged profile directory | Blank screen or a repeating sync loop | Ten minutes or more | Application support folder in the user library |
| Build for the wrong processor family | Very slow start, then a build error | Two minutes | Published builds on the official page |
Rows one and five point at the system or the package and are cleared by upgrading or by fetching the correct build. Rows two and three point at the file or at a running security tool, so a reinstall helps only in the second case and never in the third. The fourth row is the expensive one: the encrypted data store sits in that folder, so moving it aside is safe while deleting it is irreversible without a recovery phrase.
Separating a silent exit from a stalled window
A window that appears and then freezes proves the release check passed, because the process already loaded its frameworks and drew a frame. Failures at that stage come from network calls, a blocked helper service or a profile the application can’t read. Watching whether the dock icon bounces once and vanishes, or stays and stalls, splits the diagnosis in half.
When a reinstall hides the real cause
Reinstalling refreshes the bundle and often clears a quarantined download, which makes it look like a universal fix. On a release shortfall, the fresh copy hits the same gate and produces the same silent exit, and on a blocked helper service the new copy stalls at the same step. The misleading part is the extra time: two installs and a reboot can pass before anyone reads the About panel.
Limits and Costs of Forcing a Higher System Release
Upgrading the operating system to clear the gate carries costs of its own: older Intel hardware runs the newer release more slowly, some peripherals lose driver support, and an interrupted upgrade can leave the encrypted data store unreachable. Moving the application to a second computer that already meets the published requirement is usually cheaper and always reversible.
Beta and release-candidate system builds
A beta or release-candidate system build reports a version number that sorts above the stable release, so the launcher starts, yet the frameworks underneath are unfinished and can crash during the encrypted store handshake. Developers accept that exposure on a spare computer; on a computer holding keys, the beta path trades a known launch failure for an unpredictable one. The published floor says nothing about beta builds either way.
Hardware that caps below the published floor
Some computers sit one release short of the floor and stay there, because Apple’s newest system releases skip their processor generation. Patching the system with a community tool, or copying newer framework files into place, breaks the code signature the launcher checks and voids any support claim. The floor exists because the application links against interfaces those older releases never shipped.
Downgrade steps and what they erase
Rolling a system back means erasing the disk and restoring from a backup made on the older release, which also reverts every file changed since. A backup made on the newer release can’t be pushed onto the older one through the standard migration path, and the vendor publishes no supported downgrade method. Plan the sequence before touching the disk, because the erasure happens first and the restore is the part that fails.
How Do You Verify Your Installed Release Before Launching?
This sequence confirms whether the installed desktop release meets the floor published for the current build, using the system’s own About panel, a terminal signature check and the vendor’s download page. Have the computer in front of you, its processor family, and a browser tab pointed at the official download page before starting.
Step 1: Read the release and processor line
Click the Apple menu, choose System Settings, then General, then About, and write down both the version number and the chip or processor line. That single screen supplies the exact release string the launcher compares against, and the processor line decides which published build applies to this computer.
Step 2: Compare the number with the published minimum
Load the vendor’s download page and match the listed minimum system release against the number you wrote down. Floors rise with every major build, so a figure copied from a forum thread or a cached search result can sit several releases behind what the installer now demands.
Step 3: Confirm the processor build matches
Check whether the download offered for this processor family matches the About panel entry. A bundle compiled for the other architecture installs without complaint and then stops during loading with a build error, which reads like a version problem but isn’t one.
Step 4: Verify the signature on the downloaded bundle
In Terminal, run spctl –assess –verbose against the downloaded application bundle and confirm the result names the vendor. A rejection means the file was repackaged or truncated in transit, and the system will show its own warning long before the release check ever runs.
Step 5: Record the three facts before changing anything
Save the system release, the published minimum and the signature result in a plain text file next to the installer. Having all three in one place stops the reinstall loop and gives support staff the exact data they request first.
What Changes Between Releases, and What Do People Misread?
The supported floor, the processor families in scope and the number of background services the application installs all shift with each major build. Figures copied from an older tutorial go stale quietly, and the current values are published on the vendor’s official download page and in the release documentation shipped with each version.
Why the supported floor rises with each major build
Each new version links against newer system frameworks for encryption, networking and code signing, and those frameworks ship only with recent system releases. Raising the floor lets developers drop compatibility shims, which shrinks the bundle and reduces the crash surface. The trade-off lands on owners of older computers, who watch a working installation stop receiving updates without any warning beyond the changelog.
Permission prompts that appear only on newer releases
Recent system releases require explicit consent before an application reaches the local network or reads removable storage, and a denied prompt leaves a window that loads and then sits idle. Owners who upgraded the system around the same time as the application often blame the version, while the actual fix is a checkbox under Privacy and Security settings. Granting access and relaunching clears the stall in under a minute.
Q&A:
Ledger Live on my Mac bounces once and then closes. What should I check first?
Confirm your Mac meets Ledger Live’s minimum macOS requirement. Download the installer again from Ledger’s official website, not a third-party mirror. Move the app into the Applications folder, reboot the Mac, and open it from Applications. Check Date & Time settings so the clock is set automatically. If the app still closes, open Console and look for a crash report named Ledger Live, then contact Ledger support with that log.
After a macOS update, Ledger Live just shows a spinning wheel and never opens. How can I fix that?
Newer macOS releases can change permission prompts and background service behavior. Restart the Mac, then check whether Ledger Live has Full Disk Access or other permissions it may request under System Settings > Privacy & Security. If you use a beta version of macOS, switch back to a stable release or try another Mac; Ledger Live may not yet support beta builds. Quit any Ledger Live processes in Activity Monitor, rename the Ledger Live folder in ~/Library/Application Support to Ledger Live backup, and launch the app again. That forces a fresh local cache while your hardware wallet still holds your keys. If the window appears, re-add your accounts and reconnect the device.
macOS says Ledger Live is damaged and cannot be opened. Is it safe to allow it?
That message usually comes from Gatekeeper quarantine after a download. Remove the current copy, empty the Trash, and download Ledger Live directly from ledger.com. Then open System Settings > Privacy & Security, find the message about Ledger Live, and click Open Anyway. You can also Control-click the app in Applications and choose Open. Only do this if the file came from Ledger’s official site. If the warning returns after a clean download, check your Mac’s date and time, then try the install again.
On my Apple Silicon Mac, Ledger Live opens but freezes on the splash screen. What can I try?
Unplug the Ledger device and launch Ledger Live without it. If the app opens, the freeze may involve USB communication, so try another cable, port, or a powered hub. In Activity Monitor, quit every process with Ledger in its name, then reopen the app. Check that you installed the Apple Silicon build if Ledger offers one for your version; if you are running the Intel build through Rosetta, install Rosetta or switch to the native build. You can also move the Ledger Live folder from ~/Library/Application Support to the Desktop as a backup, then relaunch. If it still freezes, note the exact macOS version and Ledger Live version, and send a screenshot of the splash screen to support.
I reinstalled Ledger Live and it still will not open. Could security software, VPN, or leftover processes block it?
Yes. A firewall, antivirus, privacy tool, or VPN can stop Ledger Live from starting or reaching its services. Turn off each one briefly, then try opening the app. If it works, add Ledger Live to that tool’s allow list and turn the protection back on. Check Activity Monitor for Ledger Live, Ledger Live Helper, and any related background item; quit them all before reinstalling. Look in System Settings > Privacy & Security for blocked apps and in Login Items for old entries. Test from a new macOS user account to see whether the problem follows your main profile. Also confirm you have free disk space and that the system clock is correct. If none of these steps help, collect the crash log from Console, list your macOS version, Ledger Live version, and security tools, then contact Ledger support.
An in-person meeting of the EAS Executive Board took place in Riga on April, 23, 2026.
During the session, President Laura Capranica presented the 2025 activity report, outlining the main achievements and initiatives carried out over the past year. Secretary Ole Keldorf presented the EAS amended Statute, in accordance with applicable legislation. At the same meeting, Treasurer Mojca Doupona delivered the 2025 financial report, providing an overview of the organization’s financial management and stability. All these documents were carefully reviewed by the Board members and were unanimously approved, reflecting strong agreement on the work accomplished.
The Board also discussed the contribution of EAS to the development of ongoing Erasmus+ Sport Collaborative Partnerships, emphasizing their role and impact. In addition, the possibility of participating in the current call for proposals under the program was considered.
Proposals for upcoming EAS Cafés were presented and discussed, with the next event scheduled on May 18th.
Reports from the committees were also presented by Antonio Figueiredo (Scientific Committee), Ole Keldorf (NewGen Committee), and Laura Capranica (Communication Committee), highlighting the work carried out in their respective areas.
A preliminary draft of the program for the upcoming EAS Conference to be held in Oulu on October 5-7, 2026 was introduced by Risto Keskitalo, with further input provided by the Board members.
Finally, regarding the upcoming elections for the presidency and the Executive Board, it was agreed that the call for candidates will be open in second half of May.
The Members of the Executive Board were thankful to Ilvis Abelkalns (member of the EAS Board) for organizing and hosting the meeting at the University of Latvia.
On April 15 and 16, 2026, EAS was invited to attend the annual EU Sport Forum “Values, Inclusion, and Wellbeing” organized by the European Commission in cooperation with the Cyprus Ministry of Education, Sport and Youth in Phapos, Cyprus.
Mr. Normunds Popens ‐ Deputy Director-General of the Directorate-General Education, Youth, Sport and Culture (EAC) of the European Commission, and Mr. Marios Panayides ‐ Permanent Secretary, Ministry of Education, Sport and Youth of Cyprus, welcomed delegated of leading sport organisations, sport federations, European networks, and policymakers to the two-day event encompassing keynote speeches, plenary and parallel sessions, and panel discussions on relevant issues of the European Sport Model.
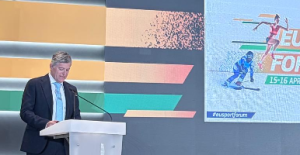
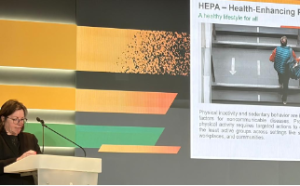 Mrs. Paola Ottomano, Team Leader, Sport Unit of the European Commission, and Mr. Luciano Di Fonzo, Deputy Head of Erasmus Mundus and Sport Unit of the European Education and Culture Executive Agency (EACEA), informed on the strategic vision for sport in Europe, including the results of the public consultation on the European Sport Model.
The thematic discussion of the first day of the event regarded: Removing barriers to women’s sporting success; Rewarding talent in sport: boosting solidarity and competitive balance; Not just medals, rethinking sport for lifelong wellbeing; The future of the European Week of Sport; The future priorities of the Irish Presidency of the Council; Uniting the Mediterranean through sport; Mental health in sport: pressure and resilience; Knowledge sharing sessions on good practices from Cyprus; Peer learning activities in Bulgaria and Slovenia; and The project GAIIN from the World Anti-Doping Agency.
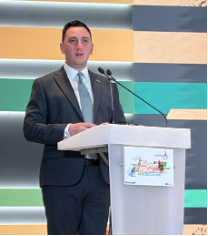
On the second day, Mr. Glenn Micallef, European Commissioner for Intergenerational Fairness, Youth, Culture and Sport, presented his personal contribution to key priorities and activities of the European Commission in the field of sport, highlighting the crucial role of physical literacy for lifelong active behaviours and health. This issue was further emphasized during the round table Move more, live better: why movement matters at every age with high-level speakers and contributors. The last two sessions were dedicated to the athletes’ experiences into sport governance roles, and the integrity and investment for the future of European basketball. Final remarks were provided by Mr. Georg Häusler, Director of Culture, Creativity and Sport of the European Commission. Further information and Recordings of the 2026 EU Sport Forum will be available at sport.ec.europa.eu.
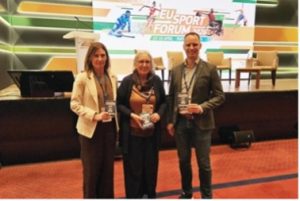
During the event, EAS and EUSA also disseminated information on the ERASMUS+Sport Collaborative Partnership “Discovering University Sport and Supporting Dual Career” (DiscoverU), which aims to encourage innovative community engagement in physical activity and healthy lifestyles among university students.

The DiscoverU project is funded by the European Union coordinated by EUSA. Views and opinions expressed are however those of the author(s) only and do not necessarily reflect those of the European Union or the European Education and Culture Executive Agency (EACEA). Neither the European Union nor EACEA can be held responsible for them.
On March 18, 2025, the European Parliament’s Committee on Culture and Education (CULT) invited European sports stakeholders at the European Parliament to contribute to a consultative meeting on the role of the EU policies in shaping the European Sport Model.
Member of the European Parliament Bogdan Zdrojewski, Vice-Chair of the CULT Committee and rapporteur of the initiative, welcomed the participants, followed by presentation by Iwona Lotysz (Polish Presidency of the Council of the European Union) Giorgio Guazzugli-Marini (Acting Head of Sport Unit at the European Commission), and Roberto Pella, (European Committee of the Regions, rapporteur of the opinion on “Building a values-based, bottom-up European sports model: a vehicle for encouraging inclusion and social wellbeing among young Europeans).
Overall, 40 stakeholders participated in the event, with 20 of them providing short speeches in contribution to the European sports policies. Laura Capranica, EAS President, highlighted the importance of European ERASMUS+Sport fundings for cooperative partnerships focused on the sportspersons’ rights to education in and through sports. She highlighted that whilst Europe has been considered a good model and inspiration for countries beyond Europe (recently, a dual career association has been established in Brazil following the EAS example), the tremendous outcomes of the ERASMUS+Sport projects do not always reach the target population at large. To bridge such a gap and to have a positive impact especially in the future generations of athletes, coaches, physical trainers, referees, sports managers, sports scholars, and volunteers, President Capranica suggested the adoption of European policies urging the sport academic institutions and the sport bodies to include relevant European priorities (such as dual career, sport inclusion, sport integrity, safeguarding, etc) in their educational courses.
Dear EAS Members and Dual Career Friends,
wishing you and your family a happy Easter, the EAS Executive Committee is pleased to update you on the recent and future activities.
Recent activities
January 24-26, the Executive Board members Ole Keldorf, António Figueiredo, and Risto Keskitalo (local organizer), conducted an official institutional visit to Oulu, Finland, the European Capital of Culture 2026, to finalize the terms of the agreement between EAS and the Kastelli Upper Secondary School to host the 23rd EAS Annual Conference next October 5-7, 2026. Further information at https://www.dualcareer.eu/institutional-visit-to-oulu-finland-in-preparation-for-the-23rd-eas-annual-conference-and-executive-board-elections-october-5-7-2026/
February 12, 2026, the EAS Executive Board launched the call of paper for the 2026 Bengt Nybelius Scholarship to facilitate the integration of outstanding scholars and young researchers up to 40 years of age in the area of dual career. Before July 1th, 2026 applicants must submit by e-mail to info@dualcareer.eu an original manuscript related to the scope of EAS. The winner will be invited to present her/his work during the EAS Conference with her/his travel, accommodation, and registration arranged by EAS. Further information at https://www.dualcareer.eu/category/news/
March 5, 2026, EAS contributed to the preparation of new proposals for ERASMUS+Sport Collaborative Partnerships coordinated by highly active and dedicated dual career partners.
March 30, 2026, the 20th virtual EAS cafè with experts and testimonials contributed to the dual career topic “Beyond Winter: Life Between Sport and Study”.

The ongoing EU-funded ERASMUS+Sport Collaborative Partnerships
DiscoverU (101134052), the Collaborative Partnership coordinated by EUSA (Slovenia) aims to enhance university sport and qualifications of elite athletes for preparing them to the labour market. After having organized Power up Workshops for Elite Athletes, events and webinars, the project entered its third year. Further information is available at https://discoveru.eusa.eu
Find Me (101134043), the Collaborative Partnership coordinated by the University of Nis aims to structure an evidence-based European user-friendly platform specifically tailored for dual career at university level. In entering its third year, a FIND ME transnational meeting was held in Ljubljana (Slovenia) on February 19-20, 2026. The European Universities willing to enhance their visibility can be included in the FIND ME platform by completing in about 5-10 minutes a survey on relevant dual career services and provisions offered to sportspersons enrolled in their courses available at https://docs.google.com/forms/d/e/1FAIpQLSepAQGxS_ftTyxQwCancqkbVibF6uYrKiQh99K1w_dTb7pgxg/viewform.
FOCUS (101243801), the Collaborative Partnership coordinated by NYSA SWEDEN AB aims to establish an innovative and scalable Dual Career co-created framework, ensuring that elite football players can successfully transition from youth to professional sport levels while maintaining educational and career opportunities. On January 22-23, 2026, the kick off meeting of the Project was organized at the Kisakallio Sports Institute (Finland).
The “Find Me” and “FOCUS” projects are co-funded by the European Union. Views and opinions expressed are however those of the author(s) only and do not necessarily reflect those of the European Union or the European Education and Culture Executive Agency (EACEA). Neither the European Union nor EACEA can be held responsible for them.
The ongoing EU-funded Citizens, Equality, Rights and Values (CERV) projects
Give Sport a Say: Give citizens a real say for the future of the EU in and through sports (101253838), coordinated by the Italian Organisation for Sports (OPES Italy) in cooperation with the European Network of Sport Education (ENSE, Austria), the EU Sport Link (Belgium), the European University Sports Association (EUSA Institute, Slovenia), The Association For International Sport for All (TAFISA, Germany), the Sports Federation Union of Catalonia (UFEC, Spain) and EAS, aims to implement 16 events across Europe to facilitate a thorough discussion and to collect ideas for an advancement of the European culture in and through sports.
The “Give Sport a Say: give citizens a real say for the future of the EU in and through sports” project is co-funded by the European Union through the Citizens, Equality, Rights and Values (CERV) Programme, within the Citizens engagement call.
Upcoming events
April 15-16, 2026: EAS will participate to the 2026 EU Sport Forum in Paphos, Cyprus, during which the future of EU sport policy, major challenges, and opportunities for cooperation at European level will be addressed. Further information is available at https://sport.ec.europa.eu/whats-new/events/eu-sport-forum-2026
April 23-24, 2026: The EAS Executive Committee will meet in Riga (Latvia) to prepare the EAS Conference, activities, and future actions.
May 2026: EAS will participate to the meeting of the EPAS Council of Europe Governing Board and joint meeting with the EPAS Consultative Committee.
August 24-28, 2026: FISU World Sport Forum “Active Body Healthy Mind: How Impactful Sport can be at Universities” to be held in Östersund (Sweden), which will encompass three subthemes: Healthy Campus – the key for Wellbeing and Excellence; University Sport Events: Driving Change Through Inclusivity and Good Governance; and Dual Career friendly Universities. Further information is available at https://www.fisu.net/events/2026-ostersund-fisu-world-forum/
August 31 to September 2, 2026: EAS will participate to the V International Seminar on Dual Career in Sport (V SIDUCA) organized by the Associação Brasileira Sobre Dupla Carreira Esportiva in Brasília (Brazil), consolidating itself as one of the leading academic and scientific forums on dual career at the international level. Further information is available at at https://www.dcbrasil.org/informações
Bengt Nybelius Scholarship
July 1 (midnight CET): To be eligible for the 2026 Bengt Nybelius Scholarship, applicants up to 40 years of age must submit their original work related to the scope of EAS by e-mail to info@dualcareer.eu. More information is available at https://www.dualcareer.eu/category/news/
Virtual EAS Cafè
Members of the dual career family are invited to suggest interesting dual career topics to be addressed during the spring, summer, fall, and winter EAS Cafè.
EAS Conference
October 5-7, 2026: the Kastelli Upper Secondary School (Finland) will host in Oulu the 2026 EAS Annual Conference, which is the most important opportunity for the members of the dual career community to elect the Executive Board Elections, and to be informed on the best practices at local, regional, and national levels, to share the findings and outcomes of EU-funded dual career projects, and to recognize the young researcher awarded the Bengt Nybelius Scholarship. The final deadline for abstract submission is September 13, 2026.
Further information will be posted on the official ES website www.dualcareer.eu and social media https://www.facebook.com/eas.dualcareer
Special thanks to the Members of the EAS Executive Committee and to the EAS family (https://www.dualcareer.eu/membership/) for their continuous commitment to the European dual career culture.
Prof. Laura Capranica,
EAS President
Dear friends of Dual Career,
On behalf of the EAS Executive Committee, I inform you that the 20th EAS Virtual Cafè on “Beyond Winter: Life Between Sport and Study” will be held on Monday March 30, 2026 (from 13:00 CET). This event is organized in conjunction with the project “Give Sport a Say” (CERV-101253838), which aims to foster the civil dialogue on future of sport policy in connection with health, equality and youth.
13:10 Welcome
Mrs. Sara Massini
Sara Massini, psychologist, is the head of European and International affair department of OPES, Italian umbrella organization for grassroots sport under the Italian Olympic Committee structure. Former secretary general of ENGSO and youth leader within the Italian youth Council and European youth forum, she has a long experience in advocacy, policy and project management in the areas of sport and youth both at National and European level.
13:10 From my dual career to the 2026 Winter Olympics and Paralympics.
Mrs. Diana Bianchedi, MD
Diana Bianchedi is gold medallist in fencing (foil) at the 1992 and 2000 Olympic Games, and at five World Championships. Graduated in Medicine and specialized in Sport Medicine, Diana is the Vice President of the Italian Olympic Committee and the Chief Strategy Planning & Legacy Officer of 2026 Milano-Cortina Olympic and Paralympic Games. She is actively supporting the dual career of athletes, being also the mother of Giulia Amore, elite fencer graduated in Economics, Management and Computer Science.
13:20 European Week of Winter Sport – from the ERASMUS+Sport project to a movement for future outlooks.
Mr. Andrej Pisl, MS
Andrej Pisl, EUSA Director of Projects and Policy, is in charge of European projects and policy, linking university sport with European values, organisations and institutions. He has over 25 years of experience in the field of sport in higher education, and currently holds a position as a Consultative Committee bureau member of the Council of Europe’s Enlarged Partial Agreement on Sport (EPAS). He is an advocate for equality, inclusion and sport for all, also actively promoting and supporting dual career pathways. Andrej holds a Master’s degree in Sport Management from the University of Ljubljana, and is currently a PhD student at the University of Rome Foro Italico.
13:30 Shooting for Two Goals: What Elite Biathletes Say About Managing Sport and Education: Preliminary Findings of the ERASMUS+Sport DC4B Project. – Prof. Małgorzata Maria Sławińska, PhD
Prof. Małgorzata Maria Sławińska, PhD, is an assistant professor and Head of the Department of Social Sciences at the Institute of Sport – National Research Institute in Warsaw. Her research interests focus on sport and physical activity psychology, with particular emphasis on the role of affect in physical activity, mental health and burnout in sport, and dual-career challenges. She is the author of peer-reviewed scientific publications and integrates theoretical and empirical perspectives with practical solutions for elite sport and the general population. She leads the Erasmus+ Sport DC4Biathletes.
13:40 The Winter Olympic Athlete’s Experience
Mrs. Anina Zurbriggen
Mrs. Anina Zuebriggen is an alpine skier, born in Switzerland, living in Bulgaria, having Bulgarian and Swiss citizenship. In 2026 she represented Bulgaria at the 2026 Winter Olympics in Milano Cortina and she is studying Biomedical Science at the University of Fribourg (SUI).
13:50 General discussions and concluding remarks
We wish you a great weekend and we look forward to meeting you for this important dual career event.
You can join the Zoom Meeting at https://uni-lj-si.zoom.us/j/97257339611 (Meeting ID: 972 5733 9611)
Feel free to share this information with your colleagues, students, coaches, sports managers, and other sport actors.
Looking forward to meeting you again!
“Give Sport a Say is funded by the European Union. Views and opinions expressed are however those of the author(s) only and do not necessarily reflect those of the European Union or the granting authority European Commission. Neither the European Union nor the granting authority can be held responsible for them.”
Under the European Citizens, Equality, Rights and Values programme (CERV), EAS joins experienced European partners (Italian Organisation for Sports – OPES Italy, Coordinator; the European Network of Sport Education – ENSE, Austria; the EU Sport Link, Belgium; the European University Sports Association – EUSA Institute, Slovenia; The Association For International Sport for All – TAFISA, Germany; the Sports Federation Union of Catalonia – UFEC, Spain) to promote the European fundamental values, democracy, and human rights, engaging citizens directly with policy-makers in a collective effort to shape the future of European sport policy.
From March 2026 to February 2028, The Give Sport a Say project (CERV-2025-CITIZENS-CIV-101253838) will implement 16 events across Europe to:
– Inform: Evaluating knowledge and explaining EU decision-making processes.
– Build Capacity: Providing practical skills and deeper insights into human rights in sport.
– Engage: Empowering citizens to contribute to policy dialogues and future EU sport strategies.
To facilitate a thorough discussion and to collect ideas for an advancement of the European culture in and through sports, the activities will be integrated into the regular sporting, educational, and governance events of the Partners.
“Give Sport a Say: give citizens a real say for the future of the EU in and through sports” project is co-funded by the European Union through the Citizens, Equality, Rights and Values (CERV) Programme, within the Citizens engagement call.
Ledger Live Not Working on iPhone: Starting the pairing again without losing accounts
Ledger Live Not Working on iPhone Solutions – begin with a forced restart of the handset, then check whether the installed build matches the current store listing, and only afterwards re-pair the signing device over the wireless link. Those three moves clear most stalls caused by suspended background processes, revoked permissions and stale pairing records. The sections below separate the failure layers, show which setups each one affects, and give a verification order that keeps your recovery phrase off the screen.
The three failure layers behind a stalled companion app
Failures cluster in three places: the handset’s operating system, the wireless link between the phone and the signing device, and the index of account data the app keeps on disk. A fault in the first layer shows as a crash on launch, the second as a pairing that drops mid-sync, the third as a balance that loads slowly or refuses to refresh.
Permission faults at the operating-system level
An app that closes the moment you tap its icon usually has a revoked permission rather than a damaged account. On Apple handsets the wireless permission lives under Settings > Privacy & Security > Bluetooth, and the per-app cellular switch sits under Settings > Cellular; a system upgrade can return either one to its default while leaving the icon and your login state intact. Low Power Mode also suspends background refresh, the mechanism the app uses to poll for new blocks, so figures appear frozen while the link itself stays healthy.
Wireless link faults between handset and signing device
Link faults show up as a pairing that completes and then drops halfway through a synchronisation pass. The handset stores a bond record for every device it has met; once the wallet firmware is updated or the unit is paired from a second phone, that record describes a handshake the accessory no longer recognises and the app keeps dialling a stale entry. Clearing the bond on both sides – delete the device inside the app, forget it in the system wireless list – forces a fresh negotiation.
Cached account data that survives a restart
The third layer is the local index the app builds from your public addresses. That index persists between launches, so a half-written record survives a reboot and keeps returning a partial balance or an endless spinner. Forcing the app closed from the app switcher clears the in-memory copy; reinstalling the build clears the copy on disk. Reinstalling costs nothing in funds, because the accounts are re-derived from the signing device, provided that device is still in your hands.
Which handsets, builds and wallet models this applies to
The guidance fits any Apple handset running a current store build of the companion software, paired with a hardware wallet that carries its own wireless radio. Cable-only signing devices talk to a desktop client instead, since the mobile application has no wired route to them. Minimum operating-system versions and the exact hardware list are published on the official source.
Radio-equipped units versus cable-only hardware
Pairing from a phone demands a signing device with an onboard radio; units that draw both power and data from a cable have nothing to pair with, which is why the mobile application reports them as absent rather than unreachable. Ownership of a cable-only unit pushes you toward the desktop client, where the wallet appears as a USB endpoint. Reading the model name on the device’s own screen is the quickest way to know which route applies to you.
Phone build versus desktop build of the same client
Both builds read the same accounts, but they age differently: the desktop client ships on a slower cadence and holds a larger local database, while the mobile build follows the store review cycle and keeps a compact index on the handset. A fault that appears in only one of the two narrows the cause to that build’s storage layer or its transport layer, and reproducing the fault in the other client is the cheapest way to tell the two apart.
Confirming your operating-system floor and app version
The store listing carries the minimum operating-system version and the current build number, and it is the only place that stays accurate; anything quoted in a forum thread ages within weeks. Read the version under Settings > General > About on the handset, compare it with the floor shown on the listing, and check the build number on the app’s own About screen. Where the handset sits below that floor, no in-app toggle will close the gap; the vendor’s support pages document the current requirements for every release.
Four routes compared when the phone client stalls
Four routes reach the same accounts: the wireless app on the handset, the desktop client over a cable, the signing device’s own screen, and a public block explorer keyed to a single address. They differ in what they can do, what they expose, and how much setup each demands, so pick by task rather than by habit.
The comparison below weighs those routes on the same four criteria: where each one runs, the limit that stops it, what it can actually do with your holdings, and the check that confirms you are looking at the right account. Balance reading, history and transaction signing are judged separately, because a route that displays a figure often signs nothing at all.
| Route | Runs on | Main limit | Check that confirms it |
|---|---|---|---|
| Companion app over a wireless pairing | Apple handset paired to a radio-equipped signing device | Needs the wireless permission granted and the wallet charged | Paired-device list shows the serial you read off the screen |
| Desktop client over a cable | Computer with a free USB port | Keeps you at a desk; the handset holds no copy | Address in the client matches the address on the device screen |
| Signing device screen alone | The hardware wallet with no host machine attached | Balances only; no history, swaps or fee estimates | Read the figure after entering the device PIN |
| Public block explorer | Any browser, with no wallet connection at all | Read-only and tied to one pasted address | Compare the explorer figure with the device screen |
The wireless app suits daily use and small transfers from a pocket; it stops fitting when the handset sits below the operating-system floor or the wallet battery has drained, and the cable client becomes the substitute. The device screen is the only route that needs no host, and it is the one to reach for when you want a figure confirmed before trusting a screen you do not control. The explorer handles a single-address lookup well and falls apart once you hold more accounts than you can paste.
What wireless pairing adds and what it hides
The radio link removes the desk but conceals the transport: pairing state lives both in the handset’s system list and in the app’s own device record, and either can go stale without a visible warning. Reviewing each transaction on the hardware screen is still required, because the phone only assembles the unsigned payload. Treat the handset as a display and a relay, never as the place where a signing decision is made.
What the cable route provides that a handset cannot
A wired connection is enumerated by the operating system as a device, so the client sees the wallet directly and the whole pairing layer drops out of the failure list. That removes one class of stale-bond faults, and it lets you review history and fees on a larger screen with a real keyboard. The trade-off is mobility, plus the need for a second machine that stays patched and whose ports remain free.
Why does wireless pairing drop right after a system update?
Operating-system upgrades rebuild the privacy permission table and restart the wireless stack, which invalidates bonds the handset held with accessories. The app then dials a device record the system no longer honours, and the connection closes a few seconds into the first synchronisation pass. Re-granting the permission and clearing both bond records restores the link.
Permission entries that reset without a prompt
Upgrades rewrite the per-app privacy table, and entries can revert to their default state without any alert reaching you. The wireless permission is listed under Settings > Privacy & Security > Bluetooth, and the cellular switch sits under Settings > Cellular; both need the app’s name switched on before any scan can succeed. When the battery drops into Low Power Mode, background refresh is suspended as well, which produces a screen that mimics a dead link almost exactly.
Stale bond records on either side
A bond record is the shared key the handset and the accessory keep after a first successful pairing. It outlives app deletion, so reinstalling the build on its own frequently changes nothing. Removing the pairing inside the app, forgetting the accessory in the system wireless list, then pairing again from scratch forces both sides to negotiate a fresh key – and the second step matters most, because the system list is the side the application cannot edit.
Does deleting the app erase my accounts?
No. Accounts derive from keys held inside the signing device, and the handset stores only an index of public addresses plus your display preferences. Deleting the build removes that index; reconnecting the wallet rebuilds it, so long as the device is still initialised and you know its unlock code. The one thing deletion does clear is any saved watchlist or portfolio view, which you would have to recreate by hand.
How do you reset and re-pair the app without losing your accounts?
Re-pairing means forcing a fresh handshake between the handset and the signing device while leaving the account list untouched. Have the wallet charged and awake, its PIN at hand, and a written copy of one account address to compare against. Nothing in this sequence asks you to type a recovery phrase, and nothing should.
Step 1: Write down one account address from the device screen
Wake the signing device and copy one receiving address exactly as its screen displays it. That written address becomes the reference you use later to prove the handset is showing the correct account rather than a cached one.
Step 2: Re-grant the wireless permission to the app
Open Settings > Privacy & Security > Bluetooth and switch the companion app on, then do the same for its cellular toggle under Settings > Cellular. A defaulted permission blocks the radio handshake before the app ever reaches the wallet, which is why the pairing screen stays empty.
Step 3: Forget the device, then delete it inside the app
Forget the signing device in the system wireless list and remove its entry from the app’s device manager. The system list holds key material the application cannot reach, so clearing only the in-app entry leaves the old bond intact and the same drop returns within a day.
Step 4: Pair again and compare the address you recorded
Start a fresh pairing from the app, approve it on the device screen, then check the address in the account list against your written copy character by character. A mismatch points to a stale local index rather than to the wireless link, which changes the next step you take.
Step 5: Reinstall from the store listing only if the fault survives
Delete the app, install it again from the official store listing, and rebuild the account list by connecting the signing device. The wallet derives every account from keys it holds internally, so this last resort risks no holdings and requires the recovery phrase to stay on paper or steel.
What stays unsettled across releases and why older advice ages
Menu names, minimum operating-system versions and the list of radio-equipped models all move between releases, and firmware has to advance alongside the app. A fix copied from a thread written two builds ago can therefore point at a setting that has since been renamed or removed. Treat every version number as something to read from the official source, rather than to recall from memory.
Firmware and app builds that drift apart
The signing device runs its own firmware, and the client speaks to it through a versioned protocol. When the app build expects a newer protocol than the wallet provides, the handset may list a device entry that refuses to synchronise while the device screen itself keeps reporting a healthy balance. Updating firmware and app so both sit on current releases is the pair that normally has to move together, and the documented update route is published on the official source.
Settings that get renamed between releases
Apple moves privacy panes and renames toggles between major versions, so a step telling you to open the wireless pane may point at a menu that carries a different label today. Searching the Settings app for the app’s own name is the durable route, because its per-app page collects the permissions wherever the system filed them. Screenshots inside older guides age faster than the surrounding text.
Claims that circulate faster than they are checked
Community threads frequently present a fix that worked once, on one build, as a permanent rule. Two claims deserve particular suspicion: that clearing the app repairs account derivation, and that a recovery phrase must be typed into the phone software to rebuild a list. Accounts come from the signing device, and no legitimate step in a vendor’s own guide asks for that phrase inside the application.
Ledger Live Not Working on iPhone Solutions can rarely be traced to one cause; the fault is usually a revoked Bluetooth permission, a stale pairing record, or a build older than the version published by the manufacturer. The order that pays off: rule out permissions first, then the bond, then the version, and treat firmware as the last suspect. Anything that asks for seed words inside a browser or a third-party tool is a dead end and a theft attempt.
Why Bluetooth Pairing Breaks Between a Handset and a Signer
Pairing breaks for three common reasons: the operating system revokes the peripheral permission after an update, the signer sleeps mid-handshake, or a cached bond goes stale once either side changes firmware. Clearing the existing record in system settings and pairing again resolves most cases faster than reinstalling anything.
Two terms matter below: a bond is the key material both ends store after a successful pairing, and a permission is the per-application grant the system keeps for Bluetooth and local-network access.
How a Low-Energy Link Is Negotiated
A wireless link begins with an advertisement the signer broadcasts and the phone scans for, followed by a key exchange that both ends save as a bond. That bond is tied to the phone’s adapter address and to the signer’s identity, so a firmware flash on the device or a radio change on the handset invalidates it while both sides still believe the pair is intact. The application reads its own stored copy of the device identifier, while the system holds the authoritative record, which is why the two can disagree after an update. Re-pairing rewrites both copies at once.
Permission Prompts Dismissed at First Launch
Bluetooth and local-network prompts appear once per installation, and declining either leaves the application unable to detect any nearby device. The system keeps those grants under privacy settings rather than inside the application, so a toggle flipped off in an earlier session survives reinstalls in some builds and produces an empty device list with no error message. Local-network access governs discovery on newer system versions; Bluetooth governs the connection itself. Both switches must be enabled before the scanner will return a result.
Stale Bond Records After a System Update
A major system release can drop bonds created under the previous radio stack, leaving the signer listed in settings while the application reports no devices in range. Forgetting the device on the handset alone leaves the signer holding an orphaned entry, and the next pairing attempt stalls at the same point. Remove the entry on both sides – in the system’s Bluetooth list and in the signer’s own pairing menu – then pair from scratch. Reusing the old record after a firmware change reproduces the fault within minutes.
Where the Mobile Companion Fits in Daily Use
Self-custody holders who sign transfers away from a desk use the phone build for approvals, firmware writes, and address checks. The wireless route applies when the signer supports radio pairing and the handset runs a system version still supported by the manufacturer; a desktop build remains the better tool for bulk account management, portfolio exports, and recovery work.
Approvals Carried Out in Transit
The signer’s screen stays the authoritative display during every transfer; the phone only relays an unsigned payload and returns a signed one. The application assembles the transaction, pushes it over the radio link, the device decodes the amount and destination on its own display, and the holder approves with the physical buttons. A link that collapses mid-approval leaves an unsigned transaction and moves no funds, so a dropped connection at that stage costs time rather than value. Repeating the flow after a fresh pairing is safe.
Firmware Writes Managed From the Phone
Device firmware can be installed through the companion application while the signer sits connected and charged. A write takes minutes and needs a stable link, so a handset that drops radio contact mid-transfer can leave the device in a bootloader state that only a wired recovery clears. Keep the signer within arm’s reach, avoid switching applications during the write, and let the battery stay well charged. Build numbers and compatibility lists are published on the official source rather than inside the application.
Accounts Guarded by an Extra Passphrase
An extra passphrase derives a separate account set, and the application displays whichever set is currently attached to the device. A holder who attaches the phrase at one session and skips it at the next sees empty balances and concludes that assets vanished, when the address list simply belongs to a different derivation. The signer prompts for the phrase at each connection unless a temporary attachment is active. Recording which phrase produces which account set prevents this confusion.
Which Recovery Route Fits Your Situation?
Match the route to the symptom: a link that drops repeatedly points to stale pairing data, an application that closes on launch points to a version mismatch, and a signer that ignores every request points to firmware or hardware. Escalation with logs comes last, once the three cheaper routes have been ruled out.
Five routes appear below, compared by how much work each demands, the limit it can never overcome, and what a holder can look at to confirm the fix took hold. Effort is measured in minutes and extra hardware, limits by the repairs a route is unable to reach, and confirmation by something visible on the signer’s own display or in the system’s settings.
| Route | Setup effort | Main limit | How to verify |
|---|---|---|---|
| System-level re-pair | Under two minutes, no extra hardware | Signer must be awake and within a metre | Device name appears in system Bluetooth settings |
| Cable link to a desktop build | A computer, a cable, and the desktop release | Phone route stays unavailable while the computer holds the link | Identical balances and accounts on the computer |
| Reinstall of the mobile build | Minutes, with keys left on the signer | Account labels and settings must be re-added | Balances reload once the signer reconnects |
| Second Apple handset | Another phone kept updated and charged | The earlier bond must be cleared first | Pairing completes on the new device only after clearing |
| Support escalation | A ticket, logs, and a waiting period | Response windows are published on the official source | Written reply quoting the ticket number |
Re-pairing suits a link that worked yesterday and fails today, and it costs nothing but a minute; it falls short when the signer refuses to appear in any scan, which shifts the problem to firmware. The desktop cable route fits bulk work and long sessions but removes the phone route for as long as the computer holds the link, and it fails a holder with no computer at hand. Reinstalling the mobile build clears cached state without touching keys on the signer, yet any account labels typed by hand must be entered again. A second handset works as a substitute while the primary is repaired, provided the older bond is cleared first. Escalation fits only after the cheaper routes have failed, and it needs logs rather than a description of the fault.
Re-pairing Versus Reinstalling the Mobile Build
Re-pairing rewrites the bond between the two radios and leaves every account label intact, while reinstalling rebuilds the application’s local database and forces the account list to be re-added from the signer. Reach for the first option when the device shows up in a scan but the connection collapses; reach for the second when the application itself closes, freezes, or fails to render balances after a re-pair. Reinstalling is the heavier step and should follow a failed re-pair, never precede it.
What Logs Make an Escalation Actionable
A support ticket moves faster when it carries the build number of the application, the system version of the handset, the firmware version of the signer, and the exact moment the connection dropped. Screenshots of the error screen and the signer’s own display remove guesswork, since the two often show different states. Reproduce the fault once with logging enabled rather than describing it from memory. Requests for seed words inside a ticket are a signal that the correspondent is an impostor.
Mistakes That Turn a Stall Into a Lockout
Cutting power during a firmware write, typing seed words into a browser or chat window, and installing builds from unverified mirrors are the three errors that convert a recoverable fault into permanent loss. The first corrupts the device’s boot state, while the other two hand control of the keys to whoever receives them.
Cables and Chargers Pulled Mid-Write
A firmware write clears and rewrites the device’s internal flash, and a supply interruption partway through leaves it without a complete image. Wireless writes hide this risk because an empty battery ends the transfer just as abruptly as a yanked cord, yet a handset that loses radio contact mid-write produces the same half-written result. The recovery path in that state is a wired reinstall of the firmware, which requires a compatible port and a desktop machine. Charge both devices before starting.
Seed Words Typed Into Browsers
The words behind the keys appear only on the signer’s own screen and are entered only when access is restored on a replacement device of the same make. Any web page, chat agent, or pop-up form requesting them is collecting control of the assets, and no legitimate support channel asks for them. Search results for connection faults are heavily targeted by such pages. Treat that request as conclusive proof of fraud and close the page.
Builds Sideloaded From Unverified Mirrors
Copies of the application offered outside the official store can carry modified code that logs the seed words entered during a restore. Signature checks exist on the store versions; a mirrored package bypasses them, and the modification rarely shows in normal use. Holders who want an older build should look for archived releases from the manufacturer rather than a file-sharing link. The same caution applies to desktop installers and browser extensions that claim to speed up a connection.
How Do You Verify a Safe Reconnection?
Work through five checks in order, using the signer’s own screen as the reference for every approval. Have the device charged, the system software updated, and a written copy of one receive address used before ready so the final comparison has something to match against.
Step 1: Confirm the mobile build matches the version published officially
Confirm the installed build number against the version listed on the vendor’s release page. A build that lags behind the published one can fail to recognise newer signer firmware, which looks like a radio fault rather than a version mismatch.
Step 2: Update the handset’s system software to a supported release
Install the latest system update available for the handset before pairing anything again. Newer system releases alter Bluetooth and local-network permission behaviour, so a pairing performed on an older build can be discarded the moment the update lands.
Step 3: Remove the existing bond from system settings
Open the system’s Bluetooth list, forget the signer, and clear its entry in the signer’s own pairing menu as well. Removing one side alone leaves a half-bond that both ends keep trying to reuse, which reproduces the original fault immediately.
Step 4: Pair again and approve the code on the signer screen
Start pairing from inside the application and enter the confirmation code displayed on the signer, never one shown on the phone. That code proves the approved device is physically present, and trusting the handset’s screen defeats the check.
Step 5: Compare one receive address against the signer screen
Display a receive address in the application and match its first and last characters against the same address on the signer. A match confirms the link is genuine, while a mismatch means something between the two screens is altering what appears.
What Changes Between OS Releases and Device Firmware
Permission rules, radio behaviour, and minimum supported versions move with every system and firmware release, so a routine that restored a link a year ago may need an extra step today. Release notes and version floors sit on the manufacturer’s official pages, and reading them before touching settings prevents most repeat faults.
Version Floors Set by the Manufacturer
Each release of the companion application declares a minimum system version for the handset and a minimum firmware version for the signer, and the pairing routine refuses to complete when either side falls below the floor. The manufacturer’s official support documentation lists those floors per release, so current numbers come from the vendor rather than from a forum post. Checking both numbers takes a minute and rules out the most frequent false diagnosis, where a holder replaces a healthy cable or repeats a pairing that was doomed by a version gap.
Permission Rules Rewritten in Newer System Builds
A system update can split one permission into two, rename a toggle, or reset grants for applications that have gone unused for a long stretch. After such a release the scanner returns an empty list until both Bluetooth and local-network access are granted again, and the settings path may sit in a different menu than before. Reviewing the privacy section after every major system update catches this before a pairing attempt fails. Older handsets that can no longer receive system updates will eventually fall below the floor.
Signer Firmware Behaviour That Shifts Between Builds
Behaviour that depends on firmware varies from one build to the next, including how the device announces itself over radio and how long it remains discoverable. A handset that connects reliably before an update and stalls after it is describing a firmware change rather than a phone fault. Such changes are documented per release, in release notes, instead of being announced inside the application. When one procedure works on a device and fails on a visually identical second one, comparing firmware build numbers usually explains the gap.
Q&A:
Why does Ledger Live close right after I tap the icon on my iPhone?
First, force quit the app: swipe up from the bottom, pause, then swipe Ledger Live away. Reboot your iPhone. Open the App Store and install any pending Ledger Live update. If it still closes, delete the app and install it again. Your crypto stays on the blockchain and on your Ledger device; the app is only a viewer. Do not enter your recovery phrase into any app or website. If the crash continues, note the iOS version and app version, then contact Ledger support.
My iPhone cannot find my Ledger Nano X in Ledger Live. What can I try?
Check that the Nano X is turned on and the PIN has been entered. Turn Bluetooth on in iPhone Settings, then open Ledger Live and allow Bluetooth permission. Do not pair the Nano X from iOS Bluetooth settings; pair it inside Ledger Live. Make sure no other phone or computer is connected to the Nano X. Turn airplane mode on for 10 seconds, then off. Reboot both the iPhone and the Nano X. If the device still does not appear, forget the Nano X in iOS Bluetooth settings if it is listed there, close and reopen Ledger Live, and try again. Keep the devices within a few feet. A low Nano X battery can also stop pairing, so charge it.
Ledger Live is stuck on Synchronizing on my iPhone and my balances are wrong. How do I fix it?
This often points to a sync or network issue rather than a problem with your crypto. Check your internet connection. Switch between Wi-Fi and cellular data. If you use a VPN, turn it off and reopen Ledger Live. Force quit Ledger Live and open it again. Pull down on the account screen to refresh. Check the account’s blockchain explorer against the balance shown in Ledger Live. If the explorer shows the same balance, the app may need time or a fresh sync. You can remove the account from Ledger Live and add it again; this does not move funds. You will need to reconnect your Ledger Nano X and approve the address check. If only one account is affected, try deleting that account and adding it back. If all accounts are stuck, reinstall Ledger Live after confirming your recovery phrase is backed up offline. Never type your recovery phrase into the app. When sync problems continue, check Ledger’s status page and contact support.
Why do sends fail in Ledger Live on iPhone after I confirm on my Nano X?
A failed send usually comes from one of a few things: network fees, connection loss, account state, or app version. Open Ledger Live and check that the account has enough balance for both the amount and the fee. Confirm you selected the correct coin and network. If the fee is too low for current network traffic, raise it if the app allows, or wait and try later. Keep the Nano X close to the iPhone during signing. If Bluetooth drops, the transaction may not broadcast. Check the transaction in a block explorer. If it is pending, wait; if it failed, the funds should stay in your account, but fees may be spent on some networks. Update Ledger Live and Nano X firmware, then reboot both devices. If sends keep failing, try a different internet connection or do the send from Ledger Live desktop with a USB cable. Contact Ledger support with the transaction ID, coin, amount, and any error message.
After an iOS update, Ledger Live will not open or Bluetooth stopped working. What should I do?
Try the basics: update Ledger Live from the App Store. Reboot your iPhone. Open Settings, find Ledger Live, and check that Bluetooth permission is allowed. If Bluetooth still fails, turn Bluetooth off and on. Remove any old Nano X entry in iOS Bluetooth settings, then pair the device again from inside Ledger Live. If the app will not open, delete it and reinstall it from the App Store. Your accounts can be added again; your funds remain on the Ledger device and blockchain. Make sure you have your recovery phrase written down offline before you remove the app. Do not share it or type it into any app, website, chat, or email. If the problem began right after an iOS beta update, wait for a Ledger Live update or use another supported phone or desktop. If none of these steps work, contact Ledger support and include your iPhone model, iOS version, Ledger Live version, and a short description of what happens.
Ledger Live Windows Installer Blocked: Why Windows Halts the Setup File
Fix Ledger Live Windows Installer Blocked by confirming the setup file’s code signature before you change any security setting: a valid signature from the publisher means the refusal is a reputation or heuristic problem, while a missing or mismatched signature means you should stop and download again. The refusal usually originates in SmartScreen’s unknown-publisher reputation lookup or in a local antivirus engine quarantining the file as it lands. Both paths are diagnosable in a few minutes with the file’s digest and its certificate chain.
How Reputation Checks Halt a Desktop Wallet Setup
Microsoft’s SmartScreen service compares a setup file’s hash and code-signing certificate against a reputation database, and a fresh build with few recorded downloads has no reputation yet, so the platform shows a warning dialog whose default button declines to run the file. Antivirus engines act earlier, scanning the file as it lands and moving it into quarantine.
Hash and Certificate Lookups
SmartScreen resolves two separate questions before the dialog appears: whether the file’s hash is known to the reputation service, and whether the signing certificate chains to a trusted root. A file can pass the second test and fail the first, which is why a correctly signed build from a well-known publisher still produces a warning in its first days. The hash lookup is per-file and resets with every rebuild, while the certificate check is per-publisher and survives version changes until that certificate expires or is rotated.
Quarantine Fires Before Any Dialog
Real-time antivirus protection intercepts the file write rather than the file execution, so an engine that flags the package removes it to quarantine before the system ever offers a run prompt. The visible result is a missing file or a truncated download instead of a warning dialog. Checking the quarantine list and the detection log is therefore the first diagnostic when a saved file disappears, and it also identifies which engine objected, since detection names differ between vendors.
Why Reputation Lags a Fresh Build
Reputation accrues from download telemetry, so a binary published minutes or hours ago has no volume behind it regardless of who signed it. Publisher-level trust reduces the friction but does not remove it, because the reputation service evaluates the specific hash. Release cadence makes this predictable: every rebuilt package with a new hash starts at zero, and the warning reappears even for users who ran the previous version without incident. A brand-new release is therefore the most likely moment to meet the refusal, not the least.
Which Machines and Setups Meet This Refusal
Default consumer protection, third-party antivirus suites and managed device policies each produce the same visible outcome through different mechanisms. Corporate laptops enforcing application control or Smart App Control are the strictest case, since a policy refusal cannot be overridden locally at all. Browsers add a mark-of-the-web tag that raises scrutiny on any downloaded executable.
Consumer Desktops With Default Protection
On a personal machine with stock settings, the refusal is nearly always a SmartScreen reputation prompt for a signed but unfamiliar build, or a third-party antivirus heuristic detection. The dialog offers a one-time override after the user opens the details panel, and that override applies only to the file that triggered it. Machines that have never altered a security setting usually need no configuration change at all; downloading again from the publisher’s own page and retrying after a short wait often clears a transient reputation miss.
Managed Devices and Application Control Policies
Policy-enforced fleets use allowlists built from publisher certificates, path rules or hash rules, and an unapproved package is declined by the policy engine rather than by SmartScreen. The user sees an administrator message with no override button, and the event is written to the device management console. Clearing it requires an administrator to add the publisher certificate or the specific hash to the policy, which is a deliberate change with audit consequences rather than a local toggle.
Fresh Releases, Portable Archives and Repackaged Builds
Version-specific downloads published hours ago, unsigned portable archives and third-party repackaged distributions meet the refusal far more often than an established release. Unsigned archives cannot pass a certificate check at all, so the only remaining test is a digest comparison against a value the publisher itself printed. Where no published digest exists, no verification path exists, and the correct action is to discard the archive rather than weaken a protection setting to accommodate it.
Official Download Routes Versus Mirrors and Repackaged Builds
Only the vendor’s own download page yields a file whose publisher certificate can be checked against the vendor’s published key. Mirrors, forum attachments, repackaged archives and repository channels each trade that check for convenience, and only a maintained repository adds a second party who reviewed the manifest before publication.
The table compares distribution routes on four criteria that decide whether verification is possible at all: whether a publisher signature survives the route, how you confirm the bytes are intact, which situation each route suits, and where it fails.
| Route | Publisher signature | How you verify | Main limit |
|---|---|---|---|
| Vendor’s own download page | Signed with the publisher’s code-signing certificate | Compare the digest and inspect the certificate chain | Heuristics can still flag a brand-new version |
| Versioned link in the vendor’s release notes | Signed by the same publisher identity | Same digest and certificate check as the main page | Older version links are retired as releases rotate |
| Maintained repository channel | Signature preserved, manifest reviewed before publication | Read the manifest’s publisher and version fields | May lag hours or days behind the newest release |
| Third-party mirror or file host | Often absent, stripped or re-signed by the host | No trustworthy reference value to compare against | Alteration is invisible from the file alone |
| Repackaged portable archive | Rarely signed at all | Only a digest the packager chose to publish | Skips the setup routine’s own integrity checks |
The vendor’s page and its versioned release links fit any first-time setup and any reinstallation, and they are the only routes where a failed signature check has a defined next step: report the mismatch to the publisher and download again. A maintained repository suits machines already managed through that channel, provided the manifest pins a version whose digest the publisher also printed; it does not suit anyone who needs a release published the same day. Mirrors and repackaged archives fit no situation where the file will hold key material, with one narrow exception – an offline machine where the digest was carried separately and compared before transfer.
What a Valid Publisher Signature Proves
A valid signature proves that the file was sealed by whoever holds the private key for that certificate, and that the bytes have not changed since sealing. It does not prove that the publisher is trustworthy, that the code is free of defects, or that the software does what its page claims. The chain matters as much as the signature: a certificate that does not chain to a trusted root, or that has passed its expiry date, fails the check even when the signature itself is intact. Verification therefore inspects the certificate details rather than only the presence of a signer name.
Why a Mirror Cannot Replace the Vendor’s Digest
A mirror can serve bytes that differ from the original by a single instruction, and the resulting file still opens and runs normally. The only defense is a reference value that did not travel with the file, which means a digest or signature obtained from a channel the mirror does not control. Downloading from a mirror and then comparing the file against that same mirror’s posted value verifies nothing, because one compromised source can supply both the payload and the matching number.
Risks of Turning Off Reputation Checks and Other Common Errors
Disabling SmartScreen or excluding a folder from real-time scanning removes the only automated check between you and a modified binary, and the exclusion stays in force long after the task that prompted it. The lower-risk path is to verify the signature and the published digest, then use the one-time run option the warning dialog itself provides.
Exclusions That Persist After the Task Is Done
An antivirus exclusion, a disabled reputation filter or a policy override set today is still active next month, and nothing in the interface reminds the user it exists. Each of those states widens the surface for every future download, not only the one that was refused. Where an exclusion is genuinely needed for a signed internal tool, scoping it to a single folder and a single file type limits the exposure, and a dated note in the change log keeps it findable later. The durable damage here is a setting nobody remembers changing.
Grabbing a Second Copy From an Unverified Source
After the first attempt is refused, the fastest apparent route is a second download from a search result or a messaging attachment rather than the publisher’s own page. That copy usually sails past the warning because it arrives unsigned or freshly re-signed, which removes the signal rather than the risk. A package carrying key material is the one file where the source matters more than the version, since an unverified copy can produce a working application and a compromised recovery phrase at the same time. Download again from the publisher instead.
Reading an Antivirus Detection as Proof of Malware
Detection labels from heuristic engines describe a code pattern rather than a confirmed threat, and freshly built or repackaged binaries trip those patterns regularly. That does not make every detection a false positive either; a detection tells you which engine objected and on what basis. Querying the label against the engine vendor’s own database separates a generic heuristic match from a named family, and comparing the file’s digest against the publisher’s printed value settles the question in practice.
How Do You Verify the Setup File Before Allowing It?
Verifying means proving that the file came from the publisher unaltered, which takes a saved copy, the digest the publisher printed for that version, and a command line that can compute one. You need the download page open, the file saved rather than executed, and roughly five minutes. No system protection feature has to be turned off.
Step 1: Save the package from the publisher’s own page
Download the file from the vendor’s official download page and save it to a local folder instead of running it from the browser’s prompt. A saved file keeps its provenance tag and can be inspected before anything executes, which is what makes the remaining checks possible.
Step 2: Compute the file’s cryptographic digest
Run a digest command such as certutil -hashfile against the saved file and note the full output string. That string is the value you compare against the publisher’s printed digest, and a single differing character means the bytes are not the ones they published.
Step 3: Inspect the signature and its certificate chain
Open the file’s properties, go to the digital signatures tab and confirm that the signer name matches the publisher and that the certificate chains to a trusted root. A signature that is present but expired, or issued to an unrelated entity, fails this check even though it looks valid at a glance.
Step 4: Check the quarantine log before downloading again
Check the security application’s quarantine and protection history for the file name and record the detection label it shows. That label identifies which engine objected and on what pattern, and it separates a quarantine event from a download that simply failed.
Step 5: Allow the verified file once, or stop if checks fail
Use the warning dialog’s details option and its one-time run choice only after the digest and the certificate both match. If either check fails, delete the file, download again from the publisher and report the mismatch rather than adjusting a system setting.
Which Details Shift Between Releases and Editions?
Certificate chains are renewed every few years, digests change with every rebuild, and dialog wording differs between system versions and editions, so any digest, file size or screenshot quoted in a forum thread goes stale within one release cycle. The durable checks are the signature chain’s trust path and the value published alongside the exact version you downloaded.
Rotating Signing Certificates
Code-signing certificates expire, and publishers rotate them without changing the product’s behaviour, so a certificate that validated last year may be replaced by one with a different serial and a different validity period. Users who saved a certificate fingerprint will see it change and mistake the change for tampering. The trustworthy reference is the publisher’s own documentation of its current signing identity, not a fingerprint captured months ago. Where a rotation happens alongside a release, both changes arrive in the same download.
Edition and Architecture Differences
The refusal behaves differently across system editions and processor architectures: consumer editions expose an override, managed editions and application-control policies do not, and an architecture mismatch produces a separate error that users often attribute to the same cause. A package built for one instruction set will not run on another at all, which is a compatibility failure rather than a security decision. Matching the published build to the machine’s architecture removes an entire class of misdiagnosis before any other check.
Faults That Persist After a Successful Setup
Some symptoms blamed on the download survive a clean installation: an application that opens and immediately closes usually points to a missing runtime dependency or a damaged local database, and a stalled sync points to network filtering rather than to the setup file. Separating these from the original refusal matters because the remedies point in opposite directions – one requires repairing the local profile, the other requires re-verifying the package. Keeping the verified file and its digest on hand turns the next diagnosis into a comparison rather than a guess.
Whitelist Ledger Live Installer in Windows Defender SmartScreen by treating the reputation prompt as a verification checkpoint, not as an obstacle to click past. The host OS, SmartScreen, and the published setup file each carry separate trust signals, and the safest allow decision combines a valid signature with a hash checked against vendor documentation.
Whitelist Ledger Live Installer in Windows Defender SmartScreen
SmartScreen compares the setup file’s reputation, publisher signature, and download origin before allowing execution. A clean signature and enough reputation can remove the prompt; an unknown file shows an override that only the user or an administrator can approve. The allowlist result is local, so another PC may still warn.
Reputation signals before an override appears
Microsoft Defender SmartScreen assembles a reputation from the file’s digital certificate, prevalence data, and the source that delivered it. A signed package from a recognized publisher reduces warnings, while a low-prevalence binary can trigger a caution even when the certificate is valid. The prompt reflects a trust score, not a verdict about the code’s intent. That distinction matters because a clean score can still hide a compromised release, and a warning can appear on a legitimate but newly published build.
Digital signature checks for the setup package
The certificate embedded in the executable binds the binary to a named entity and detects alteration after signing. SmartScreen reads that signature, checks certificate validity, and compares the publisher against its reputation store. An expired, revoked, or self-signed certificate weakens the signal, so the user sees a stronger prompt. Verification should compare the publisher string with the vendor’s release notes rather than trusting the file name alone.
Download origin and zone metadata
A file copied from the internet receives a zone identifier, sometimes called the mark of the web, which tells the host OS to apply stricter handling. Clearing that metadata through file properties can reduce one prompt, but it does not rewrite SmartScreen reputation or validate the binary. The delivery channel also matters: a package fetched from a vendor’s signed release page carries a different risk profile from one sent through chat or a mirror. Check the origin before changing any reputation setting.
Who needs to approve the desktop wallet package, and when?
A local administrator usually approves the setup package when SmartScreen raises a reputation prompt on a managed PC. Standard users may see the prompt but lack rights to override policy or change reputation controls. On personal devices, the signed-in owner can choose a one-time run; organization-managed machines may require help-desk approval. The decision applies to that device.
Standard users on locked-down machines
When group policy or endpoint management controls SmartScreen, a standard account cannot persist an allow decision. The prompt may offer no override, or the button may require an administrator credential. Submitting a request through the approved service desk creates a record and avoids sharing privileged credentials. The user should provide the exact package name, publisher, hash, and business reason so the reviewer can verify the file instead of bypassing the reputation check blindly.
Home users with a single-device decision
On an unmanaged personal computer, the account owner can approve a verified package for that machine. The allow action does not travel to another device, and a later download may receive a fresh prompt. A one-time run is narrower than disabling reputation protection, because it does not lower defenses for unrelated applications. The trade-off is repetition: every new build or altered file may need the same verification and approval cycle.
Managed fleets and central policy
In an organization, an administrator can distribute trust through application control, code-signing rules, or a reputation override that matches a publisher certificate. These mechanisms apply at scale and can be audited, but they also widen trust beyond one binary if the rule is too broad. A publisher-level exception may permit future releases without review, so the policy should include a review date, a hash allowlist where possible, and a rollback path if the vendor’s signing key is misused.
Allowlist methods compared: reputation prompt, exclusion, and verification
The narrowest method is a one-time SmartScreen approval after signature and publisher verification. Broader choices include clearing zone metadata, changing reputation-based protection, adding an antivirus exclusion, or asking the vendor for a signed release. These options differ in scope, persistence, and whether they influence SmartScreen trust. Choose the least permissive action that matches the verified file.
The table compares five allow or verification routes by best-fit situation, main limitation, and the check that confirms the file is the intended release. A hash, a fixed-length digest of the file’s bytes, is one check; a signature is another. Scope and persistence decide which route is appropriate.
| Method | Best for | Main limit | Check before use |
|---|---|---|---|
| SmartScreen allow prompt | One verified run on a personal PC | Local decision; another device may warn | Publisher signature and vendor hash |
| Zone identifier removal | Clearing download metadata on a trusted file | Does not change SmartScreen reputation | Hash match with vendor release page |
| Reputation-based protection toggle | Troubleshooting on a controlled test machine | Lowers checks for every application | Official SmartScreen documentation |
| Antivirus exclusion | Scanning conflicts with a known file | Does not bypass SmartScreen trust | Separate SmartScreen verdict |
| Vendor signature and hash check | Confirming the package is authentic | Does not alter reputation by itself | Vendor-published checksum or signed page |
A one-time prompt fits an unmanaged device where the user has already verified the binary. Zone identifier removal helps when the only obstacle is download metadata, but it is not a reputation allow. Protection toggles and antivirus exclusions are broader and should remain temporary or policy-controlled. Vendor signature and hash checks belong in every route because they answer whether the file is the intended release.
When a one-time SmartScreen allow is enough
A one-time allow is sufficient when the signature is valid, the hash matches the vendor’s published value, and the machine is not governed by a stricter policy. The approval affects that execution context, so the next download or a different device may prompt again. This narrow scope limits damage if the file was later replaced or tampered with. Record the version and hash so a future prompt can be compared instead of approved by habit.
Why antivirus exclusions do not change SmartScreen reputation
An antivirus exclusion tells Microsoft Defender’s scanning engine to skip a path or process; it does not tell SmartScreen to trust the binary. SmartScreen evaluates reputation, signature, and download origin through a separate control path. Adding an exclusion can create a false sense of safety because the file may still be halted before execution or warned about after launch. Use exclusions only for verified scan conflicts, and handle reputation through its own settings.
Risks, limits, and common mistakes with reputation overrides
The main risk is approving a tampered package that carries a valid-looking name but a mismatched hash. Reputation overrides can hide warnings for every file signed by the same publisher if the rule is broad. A local allow creates no central record, so another administrator may repeat the same decision. Verify first, approve narrowly, and document the version and hash.
Execution risk after an override
Once a binary runs, it can create files, alter settings, and contact remote services before a later scan removes it. SmartScreen is a pre-execution reputation filter, so an override moves the decision from an automated check to the user. If the package is malicious, the effects may be irreversible on that device. The safe sequence is signature and hash verification before any run approval, not after.
Local scope of allow decisions
A SmartScreen override usually applies to the current user or device and does not update a global trust database. Another machine that downloads the same file can receive the same warning, which frustrates users who expect a single permanent answer. The limitation is intentional: it prevents one person’s approval from silently authorizing the binary for everyone. Central policy is the only reliable way to apply a consistent decision across many endpoints.
False trust from a copied hash
A hash copied from a forum, chat message, or unofficial mirror proves only that two files match, not that either file is authentic. The trustworthy source is the vendor’s signed release page or a checksum published through the vendor’s official channel. An attacker can distribute a malicious package and a matching hash together. Compare against the vendor’s domain and, where available, a detached signature.
How do you verify and safely permit the wallet package through SmartScreen?
Use publisher signature checks, hash comparison, and the narrowest reputation override that allows the verified package to run. Have ready the vendor’s release page, a hash calculator, and administrative access if the PC is managed. The procedure avoids broad security changes and leaves an audit trail you can repeat.
Step 1: Confirm the publisher signature
Confirm the setup file’s digital signature against the publisher named in the vendor’s official release notes. A valid signature shows the binary was signed after compilation and has not been altered, though it does not prove the publisher’s key was not stolen.
Step 2: Compare the package hash
Compute a cryptographic hash of the downloaded package and compare it with the vendor-published value. Matching hashes confirm the file is byte-for-byte identical to the release the vendor intended to distribute.
Step 3: Open SmartScreen reputation controls
Open Microsoft Defender SmartScreen’s reputation-based protection controls before changing any allow setting. Reviewing the current state prevents an accidental broad toggle when a one-time approval or policy request would be narrower.
Step 4: Choose the least permissive override
Choose the least permissive override that matches the verification result, such as a one-time run approval. A narrow choice limits the trust change to the verified binary and avoids weakening protection for unrelated applications.
Step 5: Relaunch and confirm the package
Relaunch the application and confirm that the publisher name and version match the verified package. If the prompt returns or the publisher string differs, stop and recheck the download source rather than approving again.
What remains unsettled about SmartScreen reputation?
SmartScreen does not publish an exact reputation formula, so a prompt cannot be predicted from signature status alone. Microsoft can change prevalence thresholds, certificate handling, and policy defaults between builds. Vendor guidance can also shift as releases and signing certificates change. Treat current menu labels and thresholds as published on the official source, and verify each new package.
Reputation data is not fully transparent
The reputation score combines telemetry, prevalence, certificate reputation, and download context, but the weights and thresholds are not public. Two files with valid signatures can receive different prompts because one has broader usage history. This opacity makes user-side prediction unreliable, so verification should focus on what can be checked: signature, hash, and source. A warning does not automatically mean malware, and a clean prompt does not automatically mean safe.
Policy behavior differs by edition and management
SmartScreen settings vary across home, professional, enterprise, and education editions, and management tools can override local controls. An option visible on a personal laptop may be hidden or locked on a domain-joined workstation. The exact path and availability are published on the official source for the installed build. Administrators should confirm current policy templates instead of relying on screenshots from another version.
Vendor guidance can change without notice
A wallet vendor may rotate signing certificates, rename the executable, or move downloads to a new domain between releases. A hash or publisher string that was correct for one version can become outdated for the next. The reliable check is the vendor’s current release page, not a cached forum post. If the vendor’s guidance conflicts with SmartScreen behavior, follow the vendor’s signed release material and document the discrepancy.
Q&A:
Windows says “Windows protected your PC” when I open the Ledger Live installer. Is it dangerous, and how do I get past it?
This warning is SmartScreen. It can appear for a signed app that does not yet have enough downloads or reputation on Microsoft’s servers. First confirm the file came from https://www.ledger.com/ledger-live. Right-click the installer, choose Properties, then Digital Signatures. The signer should be Ledger SAS. If the signature is valid, click OK, then on the SmartScreen window choose More info and Run anyway. If the signer is unknown or the signature is invalid, delete the file and download it again from the official page. Do not turn off SmartScreen for all apps. That leaves your PC open to other downloads.
Bitdefender or Windows Defender removed the Ledger Live installer as a virus. Is the installer infected?
It can be a false positive. Ledger Live is signed by Ledger SAS, but antivirus engines sometimes flag installers that create drivers, access USB devices, or are new. Check the digital signature first. If it is valid and you downloaded from Ledger’s site, the file is likely clean despite the alert. You can upload the installer to VirusTotal to see which engines flag it, but do not rely on one vendor’s label. In your antivirus, allow the file or add a temporary exclusion for the installer and for %AppData%\Ledger Live. Install, then remove the exclusion and run a full scan. If the signature is missing, broken, or the publisher is not Ledger SAS, treat the file as unsafe and delete it. Never download Ledger Live from a search ad, forum link, or file-sharing site.
The Ledger Live setup file downloads, but double-clicking it does nothing. What can I check?
Silent failure usually means Windows, a security tool, or the installer itself is stopping before a window appears. Check the obvious items first: the file name should end in .exe, not .exe.txt or .crdownload. Turn on file extensions in File Explorer to see this. Right-click the file, open Properties, and if there is an Unblock checkbox at the bottom, tick it and apply. Move the installer to a simple path such as C:\Temp instead of a folder synced by OneDrive or a network drive. Right-click and choose Run as administrator. Open Task Manager and end any stale LedgerLive or installer process, then try again. If nothing changes, open Services and confirm Windows Installer and Windows Management Instrumentation are running. Look in Event Viewer under Windows Logs > Application for errors around the time you double-clicked the file; MsiInstaller entries can point to a blocked action or a missing component. You can also try a clean download from Ledger’s site while your VPN and proxy are off. If the installer still does nothing, create a new local Windows user account with administrator rights and run it there; that separates a profile problem from a system-wide block. Keep your recovery phrase offline and never enter it into any installer or support chat.
I get “This app has been blocked by your system administrator” when I try to install Ledger Live. How do I fix that on my own PC?
That message often comes from a policy rather than from Ledger Live. On a work or school laptop, AppLocker, Windows Defender Application Control, or Software Restriction Policies may block installers. In that case, ask IT for permission; changing local settings may be blocked or against policy. On a personal PC, check whether a cleanup tool, old family-safety app, or malware left a policy behind. Run gpresult /H report.html in Command Prompt and open the report to see which policies apply. You can also open secpol.msc and look under Software Restriction Policies and Application Control Policies. For local Group Policy, check Computer Configuration > Windows Settings > Security Settings > Application Control Policies and User Configuration > Administrative Templates > System for “Run only specified Windows applications.” If a policy is set and you did not create it, remove it through the tool that added it, or reset local policy with care. Do not delete registry keys at random. After a restart, try the installer again from a local folder. If the PC belongs to an employer, only IT should lift the block.
The installer starts but fails with an error code, or it freezes at “Installing.” What steps can I try?
Write down the exact error code and the step where it stops; that detail decides the fix. Begin with a restart, then close Ledger Live, Ledger Live Bridge, and any crypto-related browser extensions. Make sure you have enough free space on the Windows drive and that Windows Update is not pending a reboot. Download the newest installer from Ledger’s site, then run it as administrator. Turn off VPN, proxy, and third-party firewall filters for the install, since some blocks happen when the installer tries to reach a download server. If it freezes, open Task Manager and check whether the process is using CPU or disk; if it is idle, end it and retry. Remove leftover folders only after a failed install: %AppData%\Ledger Live, %LocalAppData%\Ledger Live, and %LocalAppData%\Programs\Ledger Live if they exist. Do not delete your wallet data unless you have your recovery phrase backed up and you understand the risk. Check Event Viewer for MsiInstaller or Application Error entries, and copy the full message for support. If the same error returns, try installing under a new local administrator account. When you contact Ledger support, share the error code, Windows version, installer version, and screenshots of the failure. Never share your 24-word recovery phrase; support will not ask for it.
REG. NUMBER: Voluntary Organisation registration VO/1270
PIC NUMBER: 913459865
Email: info@dualcareer.eu